Does business need a seatbelt or an airbag for AI?
Treasury has put a number on the gap between using AI and using it seriously. Two-thirds of Australian businesses have adopted it, fewer than one in ten significantly. That gap is a governance problem wearing a technology costume.
Treasury has just put a number on something most of us already suspected. Two-thirds of Australian businesses report they have adopted AI in some form. Fewer than one in ten report adopting it significantly. The Treasurer’s response was blunt: “We can’t just sit around and hope the benefits of AI fall into our lap. We have to reach out and take them.”
He is right to be impatient. This is the biggest productivity opportunity of our generation, and Treasury now rates AI as the first credible global growth accelerant in nearly two decades. But impatience alone will not close that gap, because the gap is not caused by a lack of enthusiasm.
Almost every executive team we speak to has people using AI. What they do not have is the confidence to let it near anything that matters , the client data, the regulated process, the decision that carries consequences. So it stays in the shallow end. A licence here, a pilot there, plenty of activity and very little productivity.
That is a governance problem wearing a technology costume.
Seatbelt or airbag?
Ask a board how it is managing AI risk and you will usually hear about an acceptable use policy, a legal review, and a plan for what to do if something goes wrong.
That is an airbag. It is passive, it sits in the steering column doing nothing, and it only earns its keep after the impact. It limits the damage of a crash you have already had.
To be clear, you want the airbag. Every organisation needs an incident response plan, a legal review, a way to contain the damage when something goes wrong. Cars carry both for a reason. The problem is when the airbag is the only control you have , because an airbag does nothing to prevent the crash.
A seatbelt is different. You engage it deliberately, before you move, every single time. It is a small piece of friction you accept at the start of the journey in exchange for being able to travel at speed.
Here is the part business leaders keep getting backwards: nobody drives slowly because they are wearing a seatbelt. The restraint is what makes the speed reasonable. Done properly, AI governance is not the handbrake on adoption , it is what lets you take your foot off the brake, because you finally know what happens if you hit something.
So what does clicking in actually look like? It is knowing which of your data is sensitive, where it is allowed to travel and which systems it must never enter. It is a defined set of approved uses, so your people know where the edges are without having to ask. It is verification of AI output before it reaches a client, a regulator or the accounts. It is clear thresholds for when a human with real authority steps in, and a named executive who owns the answer when something goes wrong. None of that is exotic. All of it has to be in place before you accelerate , not drafted afterwards in the incident review.
Faster than you can react
The reason the belt has to be on before you move is simple. You cannot brace for a crash. The impact arrives faster than human reaction time, which is exactly why the control has to be engaged in advance rather than applied in the moment.
AI now operates on those same terms. An agent can take a thousand actions in the time it takes a person to read one of them. Content is drafted, decisions are made and records are written faster than any individual can follow, let alone assess. “Human in the loop” stops being a control the moment the loop runs faster than the human in it, and quietly becomes a rubber stamp with an audit trail.
The technology itself moves at the same pace. Capability that did not exist last quarter is embedded in the tools your staff already have this quarter, usually without a procurement decision anywhere in sight. Boards meet monthly or quarterly. The ground shifts weekly. By the time a committee has formed a considered view, the thing it formed a view about has been superseded.
No organisation can out-deliberate that, and trying to is how businesses end up standing still. What you can do is build controls that hold regardless of which model sits behind them , durable decisions about data, disclosure, review and accountability that remain valid when the underlying technology changes again next month. That is the difference between a governance framework and a policy document.
The questions that stall boards
The questions are relentless, and most boards have not worked through them:
Your data. Where is it, where does it go when a model touches it, and what are the intellectual property, privacy and confidentiality implications when it gets there?
Your processes. Which ones actually need to change, which need compliance testing, and where does a human stay in the loop as a genuine control rather than a formality?
Your people. If AI writes the first draft, does the research and builds the model, how does a graduate ever learn to do those things? Treasury is already watching entry-level workers overseas for early signs of displacement. Your apprenticeship pipeline is a business risk, not an HR one.
Your costs. Tokens are cheap until they are not. Do you know what you are spending, who is spending it, and at what point a person is simply the cheaper option?
Your position. If your competitors get this right and you do not, how long before it shows up in your margin?
Underneath all of them sit the three questions every risk conversation reduces to: what can go wrong, how would we know, and what would we do about it?
In our experience it is the second one that catches organisations out. Most have some idea of what could go wrong. Very few have any way of detecting a bad AI output before a client, a regulator or an auditor does it for them.
A seatbelt is not a destination
Governance tells you how to travel safely. It does not tell you where to go, and this is where the other half of Australian business is going wrong.
Too many AI programs begin with the technology already in the room. We have the licences, now what should we do with them? That is a technology question and it produces technology answers. It is why so many pilots stall at the demonstration stage. They were never anchored to a commercial outcome, so there was nothing for them to graduate into.
The question that works is a duller one. Where does this business genuinely make and lose money? Which of those processes are constrained by how fast a person can read, write, check or decide? What would change if that constraint were removed, and what would it be worth if it were?
Start there and most of the technology choices make themselves. Start with the tool and you will spend a year proving things that were never worth doing.
Treasury’s own explanation of the productivity gap says as much: “Realising productivity gains requires investment in organisational capital, including changes to processes, business models, management practices and workforce skills.” Not licences. Not tools. Processes, business models, management practices and skills.
AI adoption is a change program, not a purchase. That is precisely why two-thirds have “some” AI and fewer than one in ten have anything significant.
Where to start
The organisations getting real value from AI are not the ones with the best tools. They are the ones that decided what they were trying to achieve, worked out where the risk actually sits, put proportionate controls around it, and trained their people to work confidently inside those controls.
That work is unglamorous, it is genuinely difficult to do from inside the business, and it benefits from an independent perspective.
Beyond Technology’s AI Governance Advisory and AI Readiness Assessment have helped organisations do exactly that , understand the strategy, plan the response and prepare the environment before the acceleration rather than after it. For mid-sized organisations without internal IT leadership, our Fractional CIO service provides the executive capability to act strategically instead of reactively.
The Treasurer is right that we cannot wait for the benefits to fall into our lap. But reaching out and taking them is a good deal easier when you are strapped in and you know where you are driving.
Not sure which one your organisation is relying on today? That is the first question worth answering, and it takes days, not months. An AI Readiness Assessment is where most of our clients start the conversation.
A 30-minute conversation with a partner is the simplest way to see where your organisation stands. No pitch, no sales process – just a senior view of where you are and where the priorities should sit.
IT Strategy Consulting aligns technology investment, governance and operations with measurable business objectives. Done properly, it creates a practical roadmap for retiring technical debt, controlling risk and improving business velocity. The advice must be independent, technology-agnostic, and actionable within the organisation’s budget, capability, legacy systems and risk appetite.
An effective IT strategy begins with business requirements, not products, platforms or vendor preferences. It defines how technology services will support growth, operational performance, customer expectations and risk management. Without that line of sight, organisations invest reactively and allow technical debt to dictate what the business can do.
The stakes become more serious as an organisation grows. Systems that worked at a smaller scale often become unreliable, fragmented or expensive. This article explains how to identify misalignment, build a growth engine approach and select genuinely independent IT strategy advice.
Key takeaways
An IT strategy roadmap creates value when it connects business priorities to technology decisions, accountable ownership and sequenced investment. It is not a wish list for new systems. It is a commercial plan that helps leaders decide what to retain, improve, replace or stop, while recognising operational constraints and the organisation’s capacity to deliver change.
Start with business outcomes and capability requirements, not a preferred technology.
Treat technical debt as a constraint on growth, resilience and operating efficiency.
Separate strategic review from product sales, implementation and managed operations.
Build a roadmap with priorities, dependencies, owners, investment logic and decision points.
Review alignment regularly rather than waiting for a contract renewal or major failure.
Measure whether technology improves business performance, not simply whether projects finish.
IT strategy alignment at a glance
A growth-oriented IT strategy connects each business objective to required capabilities, technology services, governance decisions and measurable outcomes. The comparison below distinguishes a conventional cost-centre IT management approach from an IT function designed to enable growth. The difference is not higher spending. It is clearer investment logic, stronger accountability and better sequencing.
Area
Cost-centre approach
Growth engine approach
Starting point
Existing systems and annual budget
Business objectives and capability needs
Planning
Reactive projects and vendor proposals
Deliberate, integrated technology roadmap
Investment decisions
Lowest immediate cost
Business value, risk, dependencies and whole-of-life fit
Technical debt
Deferred until failure
Identified, prioritised and progressively retired
Governance
Technology decisions remain inside IT
Business and technology leaders share accountability
Security
Separate technical programme
Business risk capability designed to respond to the inevitable breach
Advice
Influenced by incumbent suppliers
Independent and technology agnostic
Success measures
Uptime, tickets and project completion
Business velocity, reliability, adoption and realised outcomes
What is IT Strategy Consulting?
IT Strategy Consulting is the independent process of translating business objectives into technology capabilities, governance arrangements, investment priorities and an executable roadmap. It examines the current environment, defines the required future state and establishes how the organisation can close the gap without ignoring budget, operational risk, internal capability or legacy constraints.
A strategy should answer several executive questions:
What business priorities must technology support?
Which current systems enable those priorities, and which obstruct them?
Where are there capability, service, data, security and governance gaps?
What should be changed first, and what can safely wait?
Which investments depend on other work being completed?
Who owns each decision and expected business outcome?
How will leaders know whether the strategy is working?
This is broader than choosing software or preparing an infrastructure refresh. Product selection may follow, but it should not lead. Starting with a platform usually narrows the problem around what that platform can provide. Starting with the business preserves the ability to compare different operating models and technology options.
The consultant’s role is also broader than producing recommendations. Effective consultants facilitate executive decisions, challenge unsupported assumptions and convert technical issues into commercial consequences. They need to understand architecture, operations, sourcing, security and delivery. They also need to assess investment logic and organisational readiness.
At Beyond Technology, our partner consultants combine engineering qualifications with an MBA. That combination matters because an elegant architecture is not useful when the organisation cannot fund, govern or implement it. The standard is actionable advice, not a technically impressive document that sits unused.
IT strategy versus an IT plan
An IT strategy explains why particular capabilities and investments are needed. An IT plan explains what work will occur and when. The strategy provides decision principles and direction. The plan converts that direction into initiatives, dependencies, accountabilities and milestones.
Confusing the two creates a common failure mode. An organisation may have an extensive project schedule without a clear explanation of how those projects support its objectives. Activity is not alignment.
IT strategy versus enterprise architecture
Enterprise architecture describes how business, information, applications and technology fit together. It is an important input, but it is not the complete strategy. IT strategy also addresses governance, service delivery, sourcing, capability, investment sequencing, risk and the practical ability to execute.
Why IT strategies fall out of alignment
IT strategies become misaligned because business requirements change faster than governance, systems and operating practices. Growth, acquisitions, new services, regulatory obligations and workforce expectations alter what technology must deliver. When reviews are irregular, yesterday’s assumptions remain embedded in budgets, contracts and architecture long after the business has moved on.
Beyond Technology estimates that 70-90% of the IT strategies examined through its independent reviews are misaligned with current business requirements. This is an internal estimate derived from recurring patterns across its wide portfolio including professional services, education, field services and childcare case studies. The range is high because misalignment rarely appears as one failed system. It tends to accumulate across several areas.
Strategy doesn’t begin with available technology
A vendor-led discussion often starts with what a product can do. The business problem is then reframed to suit that product. This reverses the correct sequence.
Requirements should first be expressed in operational terms. For example, a field services organisation may need faster job allocation, reliable offline access and consistent information capture. Only after defining those capabilities should leaders assess applications, devices, connectivity and integration options.
Growth outpaces operational capability
Rapid growth increases users, sites, data, suppliers and support demand. It also changes the cost of outages and poor service. Informal processes that were acceptable in a small business may become significant control weaknesses at mid-sized scale.
A growing organisation can therefore appear successful while its IT function is falling further behind. Warning signs include recurring incidents, inconsistent onboarding, uncertain asset ownership, undocumented dependencies and senior staff repeatedly intervening in operational issues.
Technical debt remains invisible
Technical debt includes unsupported systems, fragile integrations, duplicated data, manual workarounds and decisions that are repeatedly deferred. Some debt is rational. Organisations cannot replace everything at once. The problem arises when leaders cannot see the debt, understand its business impact or decide which items deserve priority.
Without that visibility, legacy technology becomes the handbrake holding you back from growth opportunities. New projects cost more because teams must work around old constraints. Risk also concentrates in systems that few people understand.
Governance separates IT from the business
IT cannot remain laser focused on supporting the business when priorities are unclear or constantly contested. Technology leaders need structured access to business planning, while business executives need accountability for outcomes that depend on process, data and adoption.
A steering committee alone does not solve this. Good governance defines decision rights, escalation paths, investment criteria and outcome ownership. It also ensures that business cases account for dependencies and ongoing operating costs.
Strategy is treated as a one-off document
Alignment decays. A strategy prepared around a previous operating model will not remain relevant indefinitely. Waiting until an outsourcing contract expires leaves the organisation exposed to undetected gaps between reviews.
Independent strategic reviews should therefore occur regularly and when material business events change assumptions. Relevant triggers include rapid growth, acquisition, leadership change, repeated service failures, significant regulatory change and a major shift in technology, customer or workforce needs.
The business risks of misaligned IT
Misaligned IT restricts growth by making business change slower, less reliable and more expensive. It also obscures operational and cyber risk because leaders cannot connect ageing systems, weak processes or supplier dependencies to their commercial impact. The result is often reactive spending without a coherent improvement in organisational capability.
The most visible symptom may be poor system performance, but the deeper consequences are broader.
Lost business velocity
When systems do not support operating processes, staff create spreadsheets, duplicate data entry and manual approvals. These workarounds can keep work moving temporarily, but they make scale harder. Every additional service, location or business unit adds more exceptions.
Leaders can also be left flat footed and missing opportunities. A proposed product launch may depend on data quality, integration or security work that was never included in earlier plans. The commercial opportunity then moves faster than the organisation’s technology foundations.
Uncontrolled cost
Misalignment produces cost in places that conventional IT budgets may not expose. Examples include staff time spent on workarounds, duplicated licences, avoidable support demand, overlapping suppliers and emergency remediation.
Cost reduction alone is not the answer. Removing expenditure without understanding service dependencies can make performance worse. The objective is to direct spending towards capabilities the business needs and stop paying for complexity that creates no corresponding value.
Reduced reliability and trust
Users judge IT by whether it allows them to complete their work. Repeated interruptions, slow support and inconsistent information reduce trust. Once confidence falls, teams bypass standard systems and processes, creating more fragmentation.
Reliability is therefore not only an infrastructure issue. It depends on architecture, operational processes, supplier management, change control, support capability and realistic service expectations.
Accumulating cyber exposure
Security cannot be reduced to a collection of tools. It should operate as an immune system that combines prevention, detection, response and recovery. Business leaders must know which services are critical, what disruption would mean and how the organisation will respond to the inevitable breach.
Research has indicated an increase of over 350% in unreported business-impacting cyber security events during the last nine months of 2025. Its continuing strategic lesson is that reported incidents alone can materially understate operational exposure.
Current security planning should use recognised guidance rather than extrapolating that historical figure. The Australian Signals Directorate’s Essential Eight provides prioritised mitigation strategies. The NIST Cybersecurity Framework 2.0 also places governance alongside identification, protection, detection, response and recovery.
How IT becomes a growth engine
IT becomes a growth engine when technology investment removes constraints, strengthens reusable capability and gives the organisation a faster path from decision to execution. This requires more than modern systems. It requires deliberate alignment between business priorities, operating processes, data, architecture, workforce capability, governance and investment sequencing.
The phrase “growth engine” does not mean every technology project must produce immediate revenue. Some investments create the reliability, control or capacity needed for growth. Others reduce the time and risk involved in launching services, integrating acquisitions or entering markets.
Connect objectives to capabilities
Begin with a small set of explicit business objectives. For each objective, identify the operating capabilities required and the technology services that enable them.
Consider a hypothetical organisation expanding across Australia. Its objective might be consistent service delivery across every location. The required capabilities could include standardised workflows, central reporting, reliable connectivity, identity management and scalable support. That creates a clearer investment basis than a vague objective to “move to the cloud”.
This chain creates line of sight:
Business objective -> required capability -> technology service -> initiative -> measure -> accountable owner.
If an initiative cannot be connected through that chain, its priority should be challenged.
Retire technical debt deliberately
Retiring technical debt should compete transparently with new initiatives. Each debt item should be assessed against business impact, operational risk, security exposure, cost and the extent to which it blocks other work.
Not all debt requires immediate removal. Some can be contained, documented or monitored. The strategy should distinguish tolerated debt from neglected debt and state the assumptions supporting that decision.
Design for change capacity
A roadmap can fail even when every recommendation is correct. Organisations have finite capacity to absorb process change, migrate data, train users and manage suppliers. Projects launched simultaneously may compete for the same subject matter experts and decision-makers.
Sequencing should therefore account for organisational capacity, not only technical dependencies. A realistic roadmap may deliberately slow one initiative to protect a more valuable outcome elsewhere.
Measure business outcomes
Traditional IT measures remain useful for operational control, but they do not prove strategic value. Leaders should also examine adoption, process performance, service reliability, decision quality and whether intended capabilities are being used.
Measures must fit the objective. A customer service initiative might examine the consistency and speed of case handling. A data programme might focus on whether leaders can make defined decisions from trusted information. The purpose is not to create a large dashboard. It is to test whether investment changed business performance.
A practical IT strategy consulting process
A credible consulting process establishes the current baseline, tests it against business needs and produces an executable sequence of decisions and investments. Beyond Technology uses its RA2 Methodology and Delivery Approach: Review, Assess and Advise. Each stage reduces uncertainty while preserving a direct connection between evidence, recommendations and executive action.
Review
The Review stage mobilises the engagement, confirms principles and establishes scope. Consultants examine existing strategies, plans, contracts, architecture, service information and relevant programme artefacts. Stakeholder interviews capture different perspectives across executives, business units, users and technology teams.
The objective is not to accept every complaint as fact. It is to build a baseline view and identify where evidence, expectations and actual performance differ.
Important outputs include:
confirmed business drivers and constraints
a view of the current operating and technology environment
stakeholder expectations and unresolved decisions
known risks, dependencies and assumptions
areas requiring deeper assessment
Assess
The Assess stage benchmarks relevant capabilities, identifies gaps and examines options. Benchmarking should be contextual. A heavily regulated national organisation should not be compared uncritically with a small single-site business.
Assessment typically covers governance, service delivery, sourcing, applications, infrastructure, data, security, workforce capability and financial management. Consultants then analyse dependencies and investment logic. Options are pressure-tested against risk appetite, budget, delivery capability and likely business change.
This stage should distinguish symptoms from root causes. Frequent incidents might reflect ageing infrastructure, but they could also arise from weak change control, poor supplier accountability or unclear service ownership. Buying new equipment without diagnosing the cause may preserve the problem.
Advise
The Advise stage converts analysis into an executive-ready narrative and integrated roadmap. Recommendations should state what must change, why it matters, what it depends on and who needs to decide.
A useful final package commonly includes:
strategic principles and target capabilities
prioritised initiatives and dependencies
investment logic and assumptions
governance and operating model considerations
major risks and decision points
a sequenced roadmap
practical next actions
This is where many strategies become too abstract. A future-state diagram is not enough. Executives need a defensible path from the current environment to the desired capability.
The broader discipline is what we call IT Excellence by Design. It combines an independent IT review, effective IT governance and deliberate IT strategy. Removing one component weakens the others. Strategy without governance loses direction, while governance without independent evidence can reinforce existing assumptions.
What successful alignment looks like in practice
Successful alignment is visible when technology decisions reflect the organisation’s actual operating model, growth trajectory and risk appetite. It does not require a dramatic platform replacement. In many engagements, the most valuable outcome is a clear diagnosis, improved decision governance and a roadmap that resolves capability gaps in the right order.
The following examples come from Beyond Technology’s work.
Independent direction for a growing professional services organisation
A professional services organisation had grown consistently across diverse business units. It received regular IT advice, but lacked independent strategic direction. Beyond Technology conducted a vendor-agnostic review aligned to the requirements of individual business units and the organisation’s growth trajectory.
The resulting strategy improved organisational efficiency, reliability and trust in the fit of deployed systems. The important distinction was independence. Recommendations were not tied to an implementation contract or product outcome.
Assessing an IT function that had not kept pace
Another professional services firm had moved rapidly from a small organisation to a mid-sized business. Its IT operations had not kept pace. Beyond Technology assessed service levels, business alignment and operational capability at the organisation’s new scale.
The review identified gaps between IT service delivery and business requirements. That diagnosis gave decision-makers a grounded basis for improvement rather than relying on assumptions formed when the firm was smaller.
Telecommunications strategy for a national operator
A large national childcare and preschool operator needed to understand telecommunications capability gaps across its footprint. Beyond Technology developed a tailored telecommunications strategy and procurement framework.
The engagement remediated significant reliability problems and eliminated uncontrolled costs. It demonstrates why procurement should follow strategy. Clear requirements and an independent assessment create a stronger basis for supplier evaluation than asking the market to define the problem.
Strategic review for a Queensland university
A Queensland-based university required an independent, business-focused review of its IT function. The assessment examined alignment with broader business and academic objectives rather than treating technology as a separate operational domain.
The review provided clear strategic direction intended to improve user trust and satisfaction. In a complex institution, that shared direction is essential because technology decisions affect administration, teaching, research and support services differently.
Why vendor-provided strategy is poor governance
A vendor, reseller or operations provider cannot offer genuinely independent IT strategy when it has a commercial or reputational stake in the outcome. This is a structural conflict, not a criticism of individual competence. Technology-agnostic advice requires separation between strategic assessment and the sale, implementation or operation of recommended solutions.
Pre-sales teams are paid to sell products. Implementation partners benefit when recommendations create delivery work. Managed operations providers may be asked to assess services they designed or currently operate. Each party can contribute useful technical information, but none should control the independent strategic conclusion.
Retaining an operations provider for strategic roadmap assistance reinforces blindspots and creates inevitable conflicts of interest. A provider may be reluctant to expose weaknesses in its service model. It may also favour investments that fit its capabilities, contracts or preferred platforms.
The governance principle is straightforward: the party diagnosing the environment should not benefit from prescribing a particular product or implementation pathway.
A genuinely independent adviser should be able to recommend:
retaining an existing platform when it remains fit for purpose
changing an operating process before buying technology
renegotiating or replacing a supplier
delaying an investment until a dependency is resolved
selecting an option the adviser does not sell or implement
stopping a project that lacks a defensible business requirement
Independence also improves executive confidence. Leaders can examine trade-offs without wondering whether the recommendation was shaped by a downstream sales target.
The overlooked issue: strategy quality depends on decision quality
The overlooked weakness in many IT strategies is not architecture. It is unresolved executive decision-making. Organisations often request a roadmap while avoiding clear choices about priorities, risk appetite, ownership and investment. A consultant can document options, but no strategy will remain actionable if leaders refuse to make the trade-offs it requires.
Our position is that an IT strategy should be judged by the decisions it enables. The document is secondary. If executives cannot use it to approve, defer, sequence or stop investment, it has not done its job.
This explains why technically sophisticated strategies can fail. They may describe an attractive future state while leaving critical questions unanswered:
Which objective takes priority when funding is constrained?
What level of operational disruption is acceptable during change?
Which executive owns business adoption?
Which legacy risks will be tolerated temporarily?
What evidence would cause the roadmap to change?
Who can stop an initiative that no longer supports the strategy?
A useful strategy makes these decisions visible. It records assumptions and establishes review points. It also gives leaders permission to change the roadmap when business conditions change without abandoning the strategic principles behind it.
This is why we reject the idea that strategy is an occasional planning exercise tied to contract renewal. Technology services, business requirements and supplier performance drift continuously. Regular independent review is a governance control that detects that drift before it becomes a constraint or crisis.
How to choose an IT strategy consulting firm
Choose an IT strategy consulting firm by testing independence, commercial understanding, technical depth and the practicality of its delivery approach. The firm should explain how it moves from evidence to recommendations, manages conflicts and builds an executable roadmap. Brand recognition or product certification alone does not establish strategic capability.
Ask prospective advisers the following questions.
Do you sell or implement what you recommend?
If the answer is yes, the advice is not fully independent. Ask how commercial conflicts are disclosed and managed. Better still, separate the strategic engagement from procurement and implementation.
How will you connect recommendations to business objectives?
Look for a method that begins with stakeholder requirements, operating capabilities and commercial constraints. A catalogue of technical assessments is not enough.
Who will perform the work?
Confirm the qualifications and experience of the actual consulting team, not only the people presenting the proposal. Effective strategy work requires technical credibility and commercial judgement.
What will the final roadmap contain?
Expect priorities, dependencies, assumptions, governance, investment logic and immediate decisions. Avoid engagements that promise only a maturity score, generic target state or unprioritised list of issues.
How will uncertainty be handled?
Consultants should distinguish verified findings from assumptions. They should also identify decisions that depend on further discovery, procurement or proof-of-concept work. False certainty creates fragile plans.
Can the strategy be executed within our constraints?
Recommendations should recognise budget, internal capability, risk appetite, legacy systems and change capacity. The right answer is not necessarily the most advanced architecture. It is the approach that delivers required capability through a practical, defensible sequence.
Review your IT strategy before misalignment becomes a constraint
An independent IT strategy review gives executives evidence about whether technology services can support current objectives and future growth. It exposes capability gaps, technical debt, governance weaknesses and supplier conflicts before they force reactive decisions. The output should be a practical roadmap shaped by business priorities rather than a vendor’s product catalogue.
Do not wait for an outsourcing renewal, major outage or failed programme. Those events may trigger scrutiny, but by then the organisation has already carried the cost and risk of misalignment.
Beyond Technology provides independent, technology-agnostic IT strategy reviews. We do not need to make a product fit the requirement or create implementation work from the recommendation. Our focus is to turn your IT function from a cost centre to a growth engine through clear evidence, commercial reasoning and actionable advice.
Contact Beyond Technology to discuss an independent external review of your technology strategy, operating environment and roadmap. The first objective is clarity: what the business needs, where current capability falls short and which decisions should come next.
Frequently asked questions
IT strategy questions usually focus on scope, timing, independence and practical outputs. The answers below address the issues executives should resolve before commissioning a review. The central principle remains consistent: strategy should begin with business requirements and produce decisions the organisation can execute within its actual commercial, operational and risk constraints.
What does an IT strategy consultant do?
An IT strategy consultant assesses business objectives, technology capability, governance, services, risk and investment priorities. The consultant identifies gaps, evaluates options and produces a practical roadmap. A credible adviser also explains dependencies, assumptions, ownership and investment logic rather than providing only a technical target state.
How often should an IT strategy be reviewed?
IT strategy should be reviewed regularly and whenever material business assumptions change. Rapid growth, acquisition, new regulation, leadership change, repeated service failures or major shifts in customer requirements are valid triggers. Waiting for a supplier contract renewal allows misalignment and technical debt to accumulate undetected.
Can our managed IT provider develop our strategy?
A managed provider can supply operational evidence and technical input, but it should not independently assess services it operates. The provider has a financial and reputational interest in the outcome. Strategic review should be separated from operations, product sales and implementation to protect governance and preserve technology-agnostic advice.
What should an IT strategy roadmap include?
The roadmap should include prioritised initiatives, dependencies, accountable owners, investment assumptions, risks, governance requirements and decision points. It should connect each initiative to a business objective and required capability. It should also recognise delivery capacity so that the organisation does not approve more change than it can absorb.
Is IT strategy only for large organisations?
No. Any organisation dependent on technology can benefit from deliberate strategy. The scope should match its size and complexity. Growing organisations often need a review because informal systems, support processes and supplier arrangements may no longer fit their scale, risk profile or service expectations.
How is IT strategy success measured?
Success is measured by whether technology enables the intended business outcomes. Relevant measures may include service reliability, process performance, adoption, risk reduction and the organisation’s ability to deliver new capabilities. Project completion and technical uptime are useful operational measures, but they do not prove strategic value on their own.
References
These sources provide recognised governance, cyber security and digital service guidance relevant to IT strategy. They should inform assessment and control design, but they do not replace organisation-specific analysis. A practical strategy must interpret external guidance through the organisation’s objectives, obligations, operating model, capability and risk appetite.
Beyond Technology internal case study portfolio and business data supplied for this article, covering professional services, education, field services and childcare engagements.
{ “@context”: “https://schema.org”, “@type”: “FAQPage”, “mainEntity”: [ { “@type”: “Question”, “name”: “What does an IT strategy consultant do?”, “acceptedAnswer”: { “@type”: “Answer”, “text”: “An IT strategy consultant assesses business objectives, technology capability, governance, services, risk and investment priorities. The consultant identifies gaps, evaluates options and produces a practical roadmap with dependencies, assumptions, ownership and investment logic.” } }, { “@type”: “Question”, “name”: “How often should an IT strategy be reviewed?”, “acceptedAnswer”: { “@type”: “Answer”, “text”: “IT strategy should be reviewed regularly and whenever material business assumptions change. Relevant triggers include rapid growth, acquisition, new regulation, leadership change, repeated service failures and major shifts in customer requirements.” } }, { “@type”: “Question”, “name”: “Can our managed IT provider develop our strategy?”, “acceptedAnswer”: { “@type”: “Answer”, “text”: “A managed provider can supply operational evidence and technical input, but it should not independently assess services it operates. Strategic review should be separated from operations, product sales and implementation to protect governance and preserve technology-agnostic advice.” } }, { “@type”: “Question”, “name”: “What should an IT strategy roadmap include?”, “acceptedAnswer”: { “@type”: “Answer”, “text”: “An IT strategy roadmap should include prioritised initiatives, dependencies, accountable owners, investment assumptions, risks, governance requirements and decision points. Every initiative should connect to a business objective and required capability.” } }, { “@type”: “Question”, “name”: “Is IT strategy only for large organisations?”, “acceptedAnswer”: { “@type”: “Answer”, “text”: “No. Any organisation dependent on technology can benefit from deliberate IT strategy. The scope should match its size and complexity, with particular attention required when growth has outpaced systems, support processes or supplier arrangements.” } }, { “@type”: “Question”, “name”: “How is IT strategy success measured?”, “acceptedAnswer”: { “@type”: “Answer”, “text”: “IT strategy success is measured by whether technology enables intended business outcomes. Measures may include service reliability, process performance, adoption, risk reduction and the organisation’s ability to deliver new capabilities.” } } ] } Generated by 3P Digital SEO Client Services on 3 August 2026
The Essential Eight Is Being Retired. Your Maturity Level 2 Benchmark Is About to Move.
The ASD is retiring the Essential Eight in favour of outcome-based Essentials for enterprise IT. Here is what the change means for boards that have built their cyber benchmark around Maturity Level 2.
Why every Australian board should start preparing now for the ASD’s new Essentials for enterprise IT
For the better part of a decade, the conversation about cyber security in Australian boardrooms has had a convenient anchor point. When a regulator, an insurer or a major customer asked “are we secure enough?”, the answer was increasingly framed in a single shorthand: Essential Eight Maturity Level 2. It became the de facto benchmark — the line that separated organisations taking cyber seriously from those that were not. That anchor is about to be pulled up.
On 24 June 2026, the Australian Signals Directorate confirmed it intends to retire the Essential Eight within two years, replacing it with a broader “Essentials” series. The first chapter, Essentials for enterprise IT, is open for consultation now, with feedback due by 12 July 2026. The Essential Eight will run as a live document alongside the new guidance, with the ASD signalling it will begin to deprecate the Essential Eight in around twelve months and retire it entirely at the two-year mark.
This is not a minor revision to a maturity ladder. It is a structural change to the framework that underpins how cyber risk is measured, insured and regulated in this country. Boards that treat it as a future IT problem will find themselves benchmarked against a standard that no longer exists.
Summary Table
Issue
What Is Changing
Why It Matters
What Boards Should Do Now
Retirement of the Essential Eight
The ASD has confirmed the Essential Eight will be deprecated and then retired within two years, with Essentials for enterprise IT now open for consultation
Organisations that still rely on Essential Eight Maturity Level 2 as a benchmark may find themselves tied to a standard that is losing authority
Start planning now rather than treating this as a future IT issue
Maturity Level 2 benchmark
Maturity Level 2 has become embedded in contracts, insurance, procurement, and board risk reporting
As the framework is retired, organisations will need a new way to evidence cyber maturity and resilience
Identify where Level 2 is referenced across the business and assess exposure
Shift from prescriptive controls to outcomes
The new Essentials series moves away from fixed control checklists towards outcomes and intent
Boards will need to oversee judgement-based decisions rather than rely on a single maturity score
Reframe cyber reporting around resilience, risk, and business outcomes
Governance implications
Cyber governance can no longer sit only with IT or the CIO
The board will need clearer ownership of cyber risk appetite, assurance, and decision-making
Strengthen links between IT governance, enterprise risk, and board oversight
Existing Essential Eight investment
The ASD has stated that work already completed under the Essential Eight remains relevant
Organisations do not need to start again, but they do need to translate and realign existing controls
Protect prior investment by mapping current controls to the new framework intent
Risk of overreaction
Outcomes-based frameworks create more room for interpretation
Without independent challenge, businesses may over-spend or accept overly restrictive controls that are not proportionate to actual risk
Seek unbiased, vendor-neutral advice before budgets and controls are locked in
Capability implications
Teams experienced in evidencing Essential Eight maturity may need support interpreting the new model
The new framework requires stronger translation between business risk and technical control outcomes
Ensure management has access to independent guidance and broader governance capability
Immediate board priority
The change is already underway, not theoretical
Boards that delay may face contract, insurance, regulatory, or assurance gaps as expectations shift
Take stock, adjust governance, and begin transition planning now
Why the goalposts are moving
The ASD has been candid about why. The Essential Eight was designed in 2017 — evolving from the older Top Four — for a world of on-premises enterprise IT, when cloud was still a novelty. Its controls simply do not translate cleanly to shared-responsibility models, SaaS platforms and the cloud-first architectures that almost every organisation now runs. As the ASD put it, an architecture with no cloud at all would today be a genuinely surprising one.
There is a second, more uncomfortable reason — one we have heard from clients for years. Organisations complained that the maturity requirements kept shifting beneath them. A business assessed at Maturity Level 2 one year could find itself slipping backwards the next, despite having changed nothing and despite no actual deterioration in its security posture. The ASD has now acknowledged this is real: it was absorbing new threat tradecraft into the existing maturity levels because the structure was not flexible enough to handle evolving controls separately. The new Essentials series is designed to fix that by decoupling threat-informed controls from a fixed maturity ladder.
From prescriptive controls to outcomes
The philosophical shift matters as much as the timing. The Essential Eight told you what to do — patch applications, patch operating systems, restrict administrative privileges, implement multi-factor authentication, control applications, restrict Office macros, harden user applications and back up regularly. The Essentials series shifts the emphasis towards outcomes and intent, giving organisations the flexibility to meet the guidance using whatever tools genuinely fit their environment.
Three chapters will lead the new framework: enterprise IT first, followed by operational technology and cloud, with agentic AI flagged as a possible dedicated chapter of its own. The thinking draws heavily on the ASD’s Modern Defensible Architecture work — a stronger emphasis on defence in depth and protecting your “crown jewels”, rather than a thin perimeter wrapped around everything equally.
What this means for the Essential Eight benchmark
Here is the practical problem for most organisations. Essential Eight has quietly become embedded in contracts, cyber insurance questionnaires, supply-chain assurance programs and regulatory expectations. It is written into procurement requirements and board risk appetites. As the Essential Eight is deprecated, that benchmark will lose its authority — and the parties who rely on it will need a new yardstick. It is entirely reasonable to expect insurers, regulators and large customers to begin asking about alignment to the Essentials for enterprise IT well before the Essential Eight is formally retired.
The good news — and this is important — is that the work is not wasted. The ASD has been explicit that investment made under the Essential Eight will remain relevant under the Essentials. The controls do not disappear; they are reframed. Multi-factor authentication, privileged access management, patching discipline and reliable backups are no less essential than they were last week. What changes is how that effort is structured, evidenced and assessed.
This is a management change, not just a control change
The most important shift the Essentials brings is not technical — it is managerial. The Essential Eight suited a compliance mindset: a finite checklist, an auditable maturity score, a number you could report and defend. That model let many organisations manage cyber as a periodic assessment exercise, often delegated wholesale to the IT department. An outcomes-based framework breaks that comfortable arrangement. You cannot tick your way to resilience. You have to make judgements — about what matters most, what risk you are willing to carry, and whether your defences actually hold — and those are business judgements, not just IT ones.
This reverses the direction of the conversation. The prescriptive controls of the Essential Eight effectively tell IT what to do — apply this control, reach this level, evidence it. Under an outcomes-based framework, IT will instead need to learn to ask the business what outcomes are required, and then design and confirm the controls that actually achieve them. That is a genuinely different skill: facilitation and translation between business risk and technical control, not just implementation.
It also introduces a risk that boards should watch closely. Where a framework requires interpretation, the natural instinct of a technical team — particularly one trained to chase a maturity score — is to err on the side of caution. Left unchecked, that can lead to controls that are more expensive and more restrictive than the organisation’s actual risk justifies, and, because the rationale now rests on professional judgement rather than a published checklist, it becomes far harder for the business to challenge the approach or test whether the cost and friction are warranted. Closing that gap is exactly why the outcome must be owned by the business and the interpretation tested independently.
That means the governance links between IT and the business will need adjusting. Risk appetite statements, board reporting, audit committee agendas and management assurance processes have all been built around a maturity number that is about to disappear. When the benchmark becomes “are we resilient against the threats that matter to us?” rather than “are we at Level 2?”, the conversation has to move up — from a technical metric reported to the board, to a risk position owned by the board. Technical governance frameworks that currently terminate at the CIO’s desk will need to connect more directly to enterprise risk, strategy and the appetite the board has actually set.
It also has real implications for capability. Many IT teams have spent years building deep, specific expertise in achieving and evidencing Essential Eight maturity. That skill set — valuable as it is — is calibrated to a prescriptive standard that is being retired. Understanding what an outcomes-and-intent framework means for your organisation, your architecture and your risk profile is a different discipline. There is also a structural reason to look beyond the existing team: the people who have been optimising for the old benchmark are rarely best placed to judge, objectively, what the new one demands of the business. This is precisely the point at which organisations should seek unbiased, vendor-neutral advice and external assistance — not to replace the IT department, but to give it, and the board, an independent reading of the implications before decisions and budgets are locked in.
What boards should do now
This is not a moment for panic, but it is a moment for deliberate planning. In our advisory work we are recommending five practical steps.
Take stock of where Essential Eight lives. Identify every contract, insurance policy, regulatory obligation and supplier commitment that references Essential Eight maturity, so you understand your real exposure to the change.
Protect your existing investment. Map your current Essential Eight controls to the outcomes the Essentials framework is pursuing. Most of your effort carries forward — the task is translation, not replacement.
Adjust the governance links to the business. Revisit how cyber risk is reported, owned and assured. Move the conversation from a compliance checklist to genuine resilience — what matters most, what would hurt most if lost, whether your architecture defends it in depth — and make sure that conversation reaches the board, not just the CIO.
Get an independent reading before you commit. The skills your IT team built around Essential Eight maturity are valuable but were calibrated to the old standard. Seek unbiased, external advice to interpret what the new framework means for your specific organisation — and to test that the controls being proposed are proportionate to the risk, before decisions and budgets are set.
Have a voice in the consultation, and watch cloud and OT. The enterprise IT chapter is open for feedback until 12 July 2026 via the ASD Cyber Security Partnership Program. If your risk sits in cloud platforms or operational technology, the dedicated chapters that follow may matter even more.
The independent view
Framework transitions are exactly the moments when vendors reach for their product catalogues. As an independent advisory firm, our counsel is simpler: the Essentials series rewards organisations that understand their own risk, not those that buy the most tooling. The shift from prescriptive controls to outcomes gives you flexibility — but flexibility without clear judgement becomes ambiguity, and ambiguity is easily resolved by over-spending. The organisations that navigate this well will be those that treat the next two years as a structured transition, governed at board level and informed by independent advice, rather than a last-minute scramble as the use of the Essential Eight lapses.
The benchmark is moving. The smart response is to start moving with it — deliberately, and on your own terms.
FAQs Answered
1. How should boards prepare for the retirement of the Essential Eight?
Boards should start by understanding where Essential Eight Maturity Level 2 is currently embedded across the organisation. In many cases, it appears in supplier contracts, cyber insurance requirements, procurement standards, and risk reporting. The key issue is not just technical compliance. It is whether the organisation is prepared for a benchmark that is about to lose its authority.
At Beyond Technology, we recommend treating this as a governance transition rather than a last-minute control update. Boards should seek a clear view of contractual exposure, reporting impacts, and how current cyber investments map to the outcomes the new Essentials framework is pursuing.
2. What does the new Essentials for enterprise IT framework mean for our organisation?
The new framework signals a shift away from a fixed maturity benchmark and towards an outcomes-and-intent model. For organisations, that means the focus moves from simply evidencing a prescribed level to demonstrating that controls are proportionate, effective, and aligned to the risks that matter most.
This has practical implications for governance, assurance, and board reporting. It means organisations will need to translate existing Essential Eight investments into a broader resilience conversation and ensure the business, not just IT, is involved in defining what good looks like.
3. Do we need to replace our Essential Eight program immediately?
No. For most organisations, the work already completed under the Essential Eight remains valuable. The challenge is not starting again from scratch. It is understanding how that effort carries forward into the new Essentials framework and where interpretation, governance, and evidence will need to change.
Beyond Technology helps organisations protect their existing investment while building a practical transition path. That includes identifying what still aligns, where new expectations are likely to emerge, and how to avoid unnecessary rework or overspending during the transition.
4. How can we assess our exposure if Essential Eight Maturity Level 2 is written into contracts, insurance, or procurement requirements?
The first step is to identify every place where Maturity Level 2 has been used as a formal benchmark. This often includes customer commitments, supplier agreements, cyber insurance questionnaires, internal standards, and procurement documentation. Once that exposure is mapped, the organisation can assess where those references may need to be updated, reframed, or replaced over time.
This is an area where independent advice is especially useful. The issue is not simply whether the wording changes. It is whether the organisation can still demonstrate a defensible cyber position as external stakeholders begin shifting to the new Essentials model.
5. When should an organisation seek independent advice on the move from Essential Eight to Essentials?
Organisations should seek independent advice before major decisions are locked in. That includes budget planning, cyber program redesign, contract renewal, procurement changes, and board-level reporting updates. The teams that built capability around Essential Eight maturity bring valuable experience, but they are not always best placed to independently interpret what the new framework means for the business.
At Beyond Technology, we see this as a critical moment for objective, vendor-neutral guidance. Independent advice helps boards and executives understand the implications of the change, challenge assumptions, and make proportionate decisions before cost, control, and governance positions are set.
A 30-minute conversation with a partner is the simplest way to see where your organisation stands. No pitch, no sales process – just a senior view of where you are and where the priorities should sit.
On 30 April, the Australian Prudential Regulation Authority wrote to its regulated industries (banks, insurers and superannuation trustees) calling for what it described as a step-change in how they manage AI-related risk. The letter is the most prescriptive AI-specific intervention APRA has made, and follows a targeted supervisory review conducted across all of its regulated industries late last year.
If your organisation is not directly regulated by APRA, it would be easy to file this away as someone else’s problem. That would be a mistake. APRA’s letter is, in effect, a regulator showing its working: telling the rest of the market what it considers the minimum standard for governing AI in serious organisations. Boards that ignore that signal are choosing to learn the same lessons later, at greater cost.
What APRA actually said
The headline finding is uncomfortable: governance, risk management, assurance and operational resilience practices across the regulated industries are not keeping pace with the speed, scale and complexity of AI adoption. Three observations stand out.
First, AI risk cuts across multiple domains, spanning operational resilience, cyber and information security, data governance, model risk, change control, privacy, conduct, procurement and third-party dependency, and existing change and assurance approaches are too fragmented to manage it. Continuous validation and monitoring is not consistently in place to detect model drift, bias, failure modes or control breakdowns in a timely manner.
Second, boards are engaged with the upside of AI (productivity, efficiency, customer experience) but many directors are still developing the technical literacy required to challenge management effectively on the downside.
Third, the AI supply chain is becoming a blind spot. Embedded AI features inside existing platforms, third- and fourth-party dependencies, and rapidly evolving vendor offerings are reducing transparency at precisely the moment risk is increasing.
APRA organised its expectations around four observation areas: governance, third-party supplier risk, cyber and information security, and change management and assurance. The common thread is consistency: frameworks, ownership and accountability that span the full AI lifecycle, from design through deployment to decommissioning, supported by a current inventory of AI tooling and use cases.
Why this matters beyond regulated entities
Australian regulators tend to move in formation. The Privacy Act reforms, the AI Ethics Principles, the voluntary AI Safety Standard and now APRA’s letter are converging on a common expectation: boards are accountable for the AI being used in their organisations, whether they built it, bought it, or inherited it inside a SaaS platform. For any board with a meaningful AI footprint, the practical implications are the same:
Existing risk frameworks were not designed for AI. Bolting AI risk onto a model risk policy, a cyber policy or a procurement policy in isolation is exactly the fragmented approach APRA called out. AI risk needs to be addressed as a cross-domain discipline, with clear ownership end-to-end.
Governance has to move at the pace of deployment. AI use cases are proliferating inside organisations faster than most governance forums meet. If your AI inventory does not exist, or is six months out of date, the board has no realistic line of sight.
Third-party AI is now a first-order risk. Most organisations are not building models; they are consuming AI capabilities embedded in existing platforms or accessed via APIs. Contracts, audit rights and assurance arrangements need to catch up with that reality.
Director literacy is part of the control environment. APRA’s observation that boards lack the technical literacy to challenge management effectively is a serious one. Independent, conflict-free advice, not only from the vendors selling the technology, is increasingly part of how directors discharge their duties.
What good looks like
The organisations getting ahead of this are doing four things at once. They are treating AI governance as a board-level agenda item with regular reporting on AI risks, not just AI opportunities. They are maintaining a live inventory of AI use cases, including embedded AI in third-party tools, owned by an accountable executive. They are aligning AI risk to their existing operational resilience, cyber and model risk frameworks rather than creating a parallel structure that no one quite owns. And they are investing in the technical literacy of directors and senior leaders so that challenge in the boardroom is informed, sceptical and useful.
None of this requires reinventing the organisation’s risk approach. It does require the integrated, end-to-end view that APRA found missing.
A closing thought
APRA’s letter is worth reading in full, regardless of whether you are directly regulated by it. It is one of the clearest articulations available of what a competent regulator now expects of a competent board on AI. The bar has shifted. The question for directors is not whether to respond, but how quickly and how credibly.
A 30-minute conversation with a partner is the simplest way to see where your organisation stands against the expectations regulators are now setting. No pitch, no sales process – just a senior view of where you are and where the priorities should sit.
A partner will be in touch within one business day to schedule a 30-minute conversation. No pitch, no sales process – just a senior view of where you are.
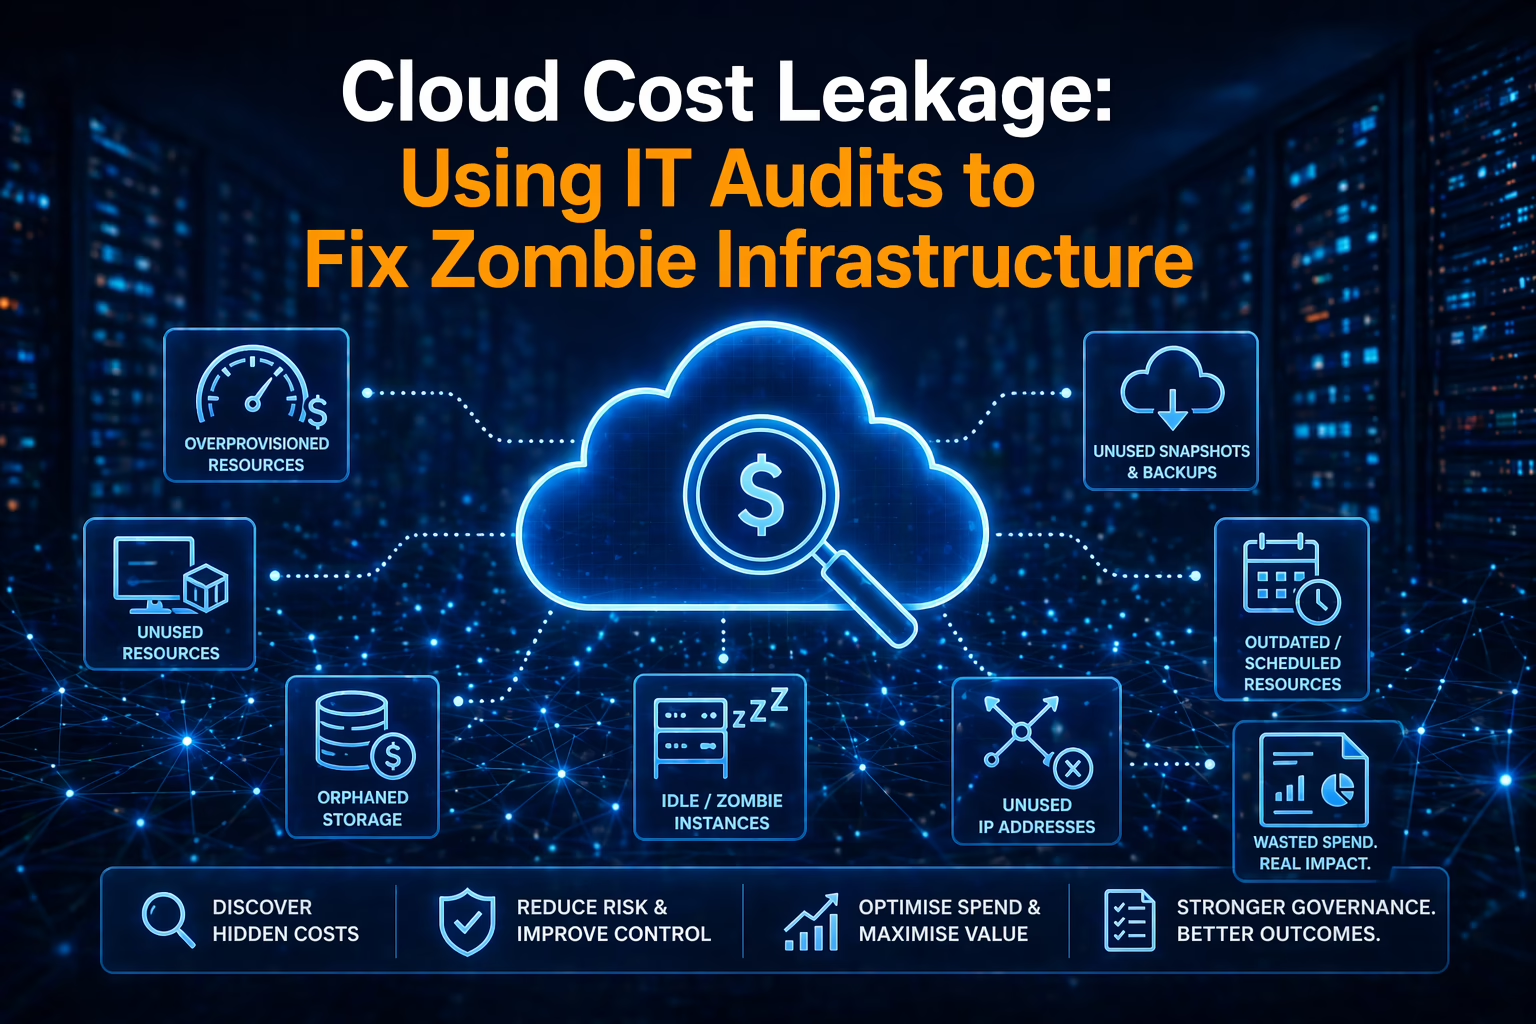
Cloud Cost Leakage: Using IT Audits to Fix Zombie Infrastructure
Azure and AWS environments quietly accumulate unused resources, oversized workloads and forgotten storage. An independent IT audit turns that invisible leakage into recoverable budget.
Cloud platforms promised flexibility, scalability, and faster delivery. For many organisations, they delivered exactly that. But over time, many Azure and AWS environments have also accumulated a quieter problem: cost leakage hidden inside unused resources, oversized workloads, forgotten storage, duplicated services, and licensing & infrastructure that no longer serve a meaningful business purpose.
At Beyond Technology, we see this as more than a budgeting issue. It is a governance issue. When SaaS licences and cloud environments grow without clear ownership, lifecycle discipline, and regular independent review, waste becomes normalised. Teams get used to paying for resources they no longer need, while executives lose visibility over whether cloud spend is supporting business outcomes or simply funding technical drift.
That is why cloud cost leakage deserves the same scrutiny as any other control weakness. An IT audit can reveal where zombie infrastructure and licences are draining budget, where provisioning standards have slipped, and where poor oversight is increasing both financial and operational risk. For CFOs, CIOs, and business leaders under pressure to improve efficiency, the opportunity is not just to cut costs. It is to create a more accountable, secure, and disciplined cloud environment.
Summary Table
Cost Leakage Area
Common Cause
Business Impact
What an IT Audit Should Test
Likely Improvement Opportunity
Idle compute resources
Virtual machines or instances left running after projects, testing, or seasonal demand
Clean up redundant backups and align retention to business requirements
Why Cloud Cost Leakage Is a Governance Problem, Not Just a Billing Problem
Cloud cost leakage is often dismissed as a billing inefficiency. In our experience at Beyond Technology, that framing is too narrow. Uncontrolled cloud spend is usually a symptom of something more fundamental: weak and immature governance over how infrastructure is provisioned, owned, reviewed, and retired.
When Azure and AWS environments grow quickly, resources are often created to solve immediate operational needs. That makes sense in the moment. The problem starts when those resources remain in place without clear accountability, regular review, or any discipline around lifecycle management. Over time, unnecessary spend becomes embedded in business as usual. Idle compute keeps running, storage keeps accumulating, and test environments remain active long after the original need has passed.
For CFOs and executive teams, this matters because it is not just about waste. It is about control. If cloud costs cannot be clearly explained, allocated, and justified, there is usually a broader visibility issue in the environment. That same lack of oversight can affect security, resilience, procurement discipline, and decision-making quality.
A well-run IT audit helps bring those issues into view. It tests whether cloud spend reflects deliberate business choices or whether it has drifted beyond effective governance. In that sense, reducing cloud cost leakage is not simply a cost-saving exercise. It is part of restoring accountability to the cloud operating model.
What Zombie Infrastructure Looks Like in Azure and AWS
Zombie infrastructure is the cloud estate that keeps consuming budget without delivering corresponding business value. In Azure and AWS, it often builds up gradually rather than through any single major mistake. A project spins up extra capacity to meet a deadline. A development team leaves a test environment running for convenience. Backups, snapshots, disks, and storage volumes are retained long after the system they supported has been retired. None of it looks serious in isolation, but collectively it becomes a significant source of waste.
At Beyond Technology, we typically see zombie infrastructure appear in a few predictable forms. There are virtual machines and instances with low or no meaningful utilisation. There are oversized workloads that were provisioned for peak demand and never rightsized. There are old environments linked to pilots, migration activity, or short-term initiatives that have quietly become permanent. There are also forgotten subscriptions, duplicated services, and unattached storage assets that remain active simply because no one is clearly accountable for removing them.
The financial impact is obvious, but the governance concern runs deeper. Resources that no longer serve a valid purpose still need visibility, access control, patching discipline, and oversight. That means zombie infrastructure is not just an efficiency problem. It is also a sign that lifecycle controls are weak. Once that pattern takes hold, cloud environments become harder to govern, harder to secure, and harder to align to actual business priorities.
Why Hidden Cloud Waste Often Goes Undetected Internally
One of the reasons cloud cost leakage becomes so persistent is that it often hides inside normal operational activity. Teams are focused on delivery, uptime, change requests, security tasks, and project deadlines. In that environment, underused resources and unnecessary spend rarely announce themselves clearly. They simply remain in place month after month, gradually becoming part of the accepted cost base.
At Beyond Technology, we often find that the root cause is not a lack of effort. It is a lack of clear visibility and ownership. Different teams may provision resources for different purposes, but no single person remains accountable for reviewing whether those resources are still needed. Tagging may be inconsistent, reporting may be fragmented, and cost data may sit too far away from operational decision-making to drive action.
There is also a practical blind spot that develops over time. Internal teams become familiar with the environment and stop questioning legacy decisions, duplicated services, or long-running non-production assets. What once made sense for speed or flexibility can remain in place long after the business case has disappeared.
This is where an independent review becomes valuable. An IT audit can look at the environment with fresh discipline, review controls and Fin Ops processes, test whether cloud spend is still justified, and identify waste that internal teams may no longer see because it has become embedded in day-to-day operations.
The Link Between Cloud Cost Optimisation and Cloud Security Audit
Cloud cost optimisation and cloud security audit are often treated as separate conversations, but in practice they are closely connected. At Beyond Technology, we regularly see that the same weaknesses driving unnecessary spend also create avoidable security and governance exposure. Unused resources, forgotten environments, excessive permissions, poor asset visibility, and weak lifecycle controls do not just increase cost. They also expand the organisation’s risk surface.
A virtual machine left running without purpose still needs patching, monitoring, and access control. An old storage repository still needs governance over retention, ownership, and data sensitivity. A development environment that was never properly retired may still hold credentials, integrations, or historical data that no longer have a valid operational reason to exist. In each case, cost leakage is also evidence of weak control discipline.
This matters because cloud environments are rarely made safer by complexity. The more redundant or poorly governed infrastructure an organisation carries, the harder it becomes to maintain clear oversight. Security teams lose confidence in the asset base, executives lose confidence in reporting, and the business inherits avoidable operational risk.
That is why an effective IT audit should assess cloud waste and cloud control maturity together. For Beyond Technology, the goal is not simply to reduce the bill. It is to help clients create a leaner, more secure, and more defensible cloud environment.
What an IT Audit Should Examine in an Azure or AWS Environment
An effective cloud audit should do more than highlight a high monthly bill. At Beyond Technology, we approach cloud cost reviews by looking for the control weaknesses that allow waste to persist in the first place. The objective is to understand whether cloud spend is supported by clear governance, accountable ownership, and evidence of ongoing review.
That starts with resource utilisation. Are compute, storage, databases, and platform services being used in line with their current business purpose, or have they drifted beyond what is operationally necessary? From there, the audit should test provisioning standards, rightsizing discipline, lifecycle controls, shutdown practices for non-production environments, and whether redundant resources are being retired in a timely way.
Just as importantly, the review should assess visibility. Are subscriptions or accounts structured clearly? Is tagging consistent enough to support meaningful reporting and cost allocation? Are ownership, approvals, and review responsibilities defined? An audit should also examine the link between cost control and risk, including access governance, backup sprawl, legacy assets, and overlapping services that add both expense and complexity.
In our view, the real value of an IT audit is not just identifying wasted spend. It is exposing the governance gaps that created it, so the business can reduce cost while improving control, accountability, and confidence in the cloud environment.
How Independent Audits Help CFOs Recover Wasted Cloud Spend
For CFOs, cloud cost leakage is rarely just a technical concern. It affects budget discipline, forecasting confidence, and the credibility of technology investment decisions. When cloud spend continues to rise without a clear line of sight to business value, finance leaders are left asking whether the organisation is funding capability or simply carrying avoidable waste.
At Beyond Technology, we see independent audits play an important role here because they cut through familiarity and internal assumptions. Cloud teams are often working hard to keep environments stable and responsive, but that does not always leave room for objective review of long-running waste, duplicated services, or inherited infrastructure that no longer serves a valid purpose. An independent audit provides a clearer picture of where spend is justified, where it has drifted, and where corrective action can be taken without undermining performance.
This matters because the goal is not indiscriminate cost-cutting. It is smarter cost recovery. By identifying over-provisioned resources, inactive environments, weak ownership, and poor lifecycle control, an audit helps finance and technology leaders recover spend in a controlled way. That creates a stronger basis for reinvestment, improves the quality of budget conversations, and gives executives greater confidence that cloud costs are being governed rather than merely tolerated.
Using FinOps in Building a More Disciplined Cloud Cost Governance Model
Fixing zombie infrastructure is important, but long-term value comes from preventing the same patterns from returning. In our view at Beyond Technology, that requires a more disciplined cloud cost governance model, one that treats cloud spend as an area of ongoing control rather than a monthly bill to be reviewed after the fact.
A stronger Fin Ops model starts with clear ownership. Every environment, service, and major resource group should have accountable business or technical ownership, supported by consistent tagging and reporting standards. From there, organisations need practical lifecycle controls so that non-production environments, temporary workloads, snapshots, storage, and legacy assets are reviewed and retired when their purpose ends. Rightsizing should be routine, not occasional, and cloud reporting should give executives a meaningful view of spend against business value.
Governance also needs regular challenge. Independent review points help test whether internal controls are working, whether spend allocation is credible, and whether cost optimisation efforts are improving both efficiency and oversight. When these disciplines are in place, cloud cost management becomes more than a clean-up exercise. It becomes part of stronger financial governance, better risk control, and more accountable technology leadership.
Final Thoughts
At Beyond Technology, we see cloud cost leakage as a clear sign that governance has not kept pace with cloud growth. Platforms like Azure and AWS can deliver enormous flexibility, but without strong ownership, lifecycle discipline, and independent review, that flexibility often turns into silent waste. Idle resources, oversized environments, and forgotten infrastructure do more than erode budget. They weaken visibility, complicate oversight, and make it harder for executives to trust that technology spend is aligned with business priorities.
That is why cloud cost optimisation should not be treated as a one-off clean-up exercise. It should be approached as part of a broader IT audit and governance discipline. When organisations apply that lens properly, they do more than reduce spend. They improve accountability, tighten control, and create a cloud environment that is leaner, clearer, and easier to defend from both a financial and operational perspective.
FAQs Answered
1. How do you audit cloud cost leakage in cloud platforms such as Azure and AWS?
At Beyond Technology, we audit cloud cost leakage by looking beyond the invoice and into the control environment that sits behind it. The question is not just where money is being spent, but whether that spend is still justified by a current business need. We review resource utilisation, lifecycle controls, environment sprawl, storage growth, tagging quality, ownership, and reporting maturity to identify where waste has become embedded.
We also look at whether the environment is being actively governed. If resources are over-provisioned, left running unnecessarily, or retained without clear accountability, that is usually a sign of broader control weakness. Our role is to give clients an independent view of where cloud spend is supporting the business and where it has drifted into avoidable waste.
2. What causes zombie infrastructure in cloud environments?
Zombie infrastructure is usually created by good intentions followed by weak follow-through. Teams provision resources quickly to support delivery, testing, resilience, or project timelines, but those same resources are not always reviewed, rightsized, or retired once the original need has passed. Over time, unused compute, orphaned storage, forgotten environments, old backups, and duplicate services begin to accumulate.
In our experience, the real cause is rarely technical incompetence. It is usually a lack of ownership, inconsistent lifecycle governance, and limited independent scrutiny. Without those controls, cloud environments tend to carry far more legacy cost than most organisations realise.
3. Can an IT audit reduce cloud costs without affecting performance?
Yes, if it is done properly. At Beyond Technology, we do not see cloud cost optimisation as a blunt cost-cutting exercise. The objective is to distinguish between infrastructure that is genuinely supporting resilience and performance and infrastructure that is simply lingering without a clear purpose. A disciplined IT audit helps clients identify wasted spend in a way that protects core operations rather than undermining them.
That usually means focusing on idle resources, over-provisioned workloads, redundant services, and poor governance practices before touching anything business-critical. When handled carefully, an audit can reduce cloud costs while also improving visibility, control, and confidence in the environment.
4. What is the difference between cloud cost optimisation and a cloud security audit?
Cloud cost optimisation is typically focused on reducing unnecessary spend and improving the efficiency of cloud resources. A cloud security audit is focused on whether the environment is being governed and protected appropriately. In practice, however, the two are often closely related.
At Beyond Technology, we regularly see the same issues affecting both cost and risk. Forgotten environments, unused assets, weak ownership, poor visibility, and excessive complexity can all increase spend while also weakening security posture. That is why we believe organisations get the best outcome when they assess cloud efficiency and cloud control maturity together rather than treating them as separate issues.
5. When should a business engage an independent cloud audit provider?
An independent cloud audit is most valuable when cloud spend is rising without clear explanation, when internal teams suspect waste but lack the time or distance to assess it properly, or when executives need stronger evidence before making cost, governance, or procurement decisions. It is also useful after major migrations, periods of rapid growth, merger activity, or significant changes in the operating environment.
Beyond Technology supports clients when they need an objective view of whether their Azure or AWS environment is efficient, well governed, and aligned to business needs. In those situations, independent review helps turn cloud cost discussions from assumptions into evidence-based action.
FAQs answered
How do you audit cloud cost leakage in cloud platforms such as Azure and AWS?
At Beyond Technology, we audit cloud cost leakage by looking beyond the invoice and into the control environment that sits behind it. The question is not just where money is being spent, but whether that spend is still justified by a current business need. We review resource utilisation, lifecycle controls, environment sprawl, storage growth, tagging quality, ownership, and reporting maturity to identify where waste has become embedded. We also look at whether the environment is being actively governed. If resources are over-provisioned, left running unnecessarily, or retained without clear accountability, that is usually a sign of broader control weakness. Our role is to give clients an independent view of where cloud spend is supporting the business and where it has drifted into avoidable waste.
What causes zombie infrastructure in cloud environments?
Zombie infrastructure is usually created by good intentions followed by weak follow-through. Teams provision resources quickly to support delivery, testing, resilience, or project timelines, but those same resources are not always reviewed, rightsized, or retired once the original need has passed. Over time, unused compute, orphaned storage, forgotten environments, old backups, and duplicate services begin to accumulate. In our experience, the real cause is rarely technical incompetence. It is usually a lack of ownership, inconsistent lifecycle governance, and limited independent scrutiny. Without those controls, cloud environments tend to carry far more legacy cost than most organisations realise.
Can an IT audit reduce cloud costs without affecting performance?
Yes, if it is done properly. At Beyond Technology, we do not see cloud cost optimisation as a blunt cost-cutting exercise. The objective is to distinguish between infrastructure that is genuinely supporting resilience and performance and infrastructure that is simply lingering without a clear purpose. A disciplined IT audit helps clients identify wasted spend in a way that protects core operations rather than undermining them. That usually means focusing on idle resources, over-provisioned workloads, redundant services, and poor governance practices before touching anything business-critical. When handled carefully, an audit can reduce cloud costs while also improving visibility, control, and confidence in the environment.
What is the difference between cloud cost optimisation and a cloud security audit?
Cloud cost optimisation is typically focused on reducing unnecessary spend and improving the efficiency of cloud resources. A cloud security audit is focused on whether the environment is being governed and protected appropriately. In practice, however, the two are often closely related. At Beyond Technology, we regularly see the same issues affecting both cost and risk. Forgotten environments, unused assets, weak ownership, poor visibility, and excessive complexity can all increase spend while also weakening security posture. That is why we believe organisations get the best outcome when they assess cloud efficiency and cloud control maturity together rather than treating them as separate issues.
When should a business engage an independent cloud audit provider?
An independent cloud audit is most valuable when cloud spend is rising without clear explanation, when internal teams suspect waste but lack the time or distance to assess it properly, or when executives need stronger evidence before making cost, governance, or procurement decisions. It is also useful after major migrations, periods of rapid growth, merger activity, or significant changes in the operating environment. Beyond Technology supports clients when they need an objective view of whether their Azure or AWS environment is efficient, well governed, and aligned to business needs. In those situations, independent review helps turn cloud cost discussions from assumptions into evidence-based action.
A 30-minute conversation with a partner is the simplest way to see where your organisation stands. No pitch, no sales process – just a senior view of where you are and where the priorities should sit.
AML/CTF Tranche 2: Why Accounting and Legal Firms Need an IT Audit Now
From July 2026, AML/CTF Tranche 2 brings accounting firms, legal practices and other gatekeeper professions under AUSTRAC oversight. Compliance success will be decided by technology systems, and most firms have not audited theirs.
Australia’s AML/CTF Tranche 2 reforms will significantly expand regulatory oversight across industries that have traditionally sat outside AUSTRAC supervision. From July 2026, sectors including Accounting firms, real estate agencies, legal practices, and other professional service providers will be required to implement formal anti-money laundering and counter-terrorism financing controls.
For many organisations in these sectors, the immediate focus has been on policy documentation, staff training, and governance frameworks. While these elements are essential, they represent only part of the compliance picture. The real challenge lies in whether the technology systems supporting client onboarding, identity verification, document storage, and reporting processes are capable of meeting regulatory expectations.
Client due diligence is now largely conducted through digital platforms and integrated business systems. Property transactions, trust accounts, digital contracts, identity verification services, and CRM platforms all generate data that must be securely captured, retained, and auditable. If these systems are fragmented or poorly governed, organisations may struggle to demonstrate compliance when regulators request evidence.
An independent IT audit provides clarity in this environment. It examines whether the systems supporting compliance have appropriate governance and security controls, are properly configured, consistently enforced, and capable of producing defensible records. For professional services firms preparing for AUSTRAC oversight, this type of review helps convert policy intentions into verifiable operational controls.
As Tranche 2 approaches, real estate, accounting and legal firms must move beyond theoretical compliance frameworks and ensure their technology infrastructure can withstand regulatory scrutiny.
Summary Table
Compliance Requirement
Technology Risk
IT Audit Focus
Outcome
Client Due Diligence
Inconsistent identity verification processes across onboarding systems
Review identity verification platforms, onboarding workflows, and audit trails
Reliable and defensible client verification records
Record Retention
Client documents stored across multiple platforms without clear retention rules
Assess document storage systems and retention configuration
Consistent, traceable compliance records
Transaction Monitoring
Limited visibility across financial and property transaction data
Evaluate system logging and reporting capabilities
Improved monitoring and regulatory reporting readiness
Data Governance
Disconnected CRM, property management, and document systems
Analyse data flow and integration controls
Stronger governance and reduced data fragmentation
Compliance Oversight
Policies not reflected in system controls or review processes
Review governance frameworks and ownership of controls
Sustainable compliance operations
Independent Assurance
Internal teams lack objective visibility into system risk
Conduct independent IT governance and compliance audit
Executive confidence and regulatory preparedness
Understanding AML/CTF Tranche 2 and the Expansion of Gatekeeper Regulation
Australia’s anti-money laundering and counter-terrorism financing framework has historically focused on financial institutions, banks, and large financial intermediaries. However, global regulatory pressure and evolving financial crime risks have prompted governments to expand oversight into sectors that facilitate the movement or structuring of funds.
This expansion is known as AML/CTF Tranche 2, and it introduces compliance obligations for industries often referred to as “gatekeeper professions.” These include real estate agents, legal professionals, accountants, and other advisory services that play a role in high-value transactions or corporate structuring.
The rationale is straightforward. Criminal networks increasingly rely on professional intermediaries to move assets, purchase property, establish entities, or obscure beneficial ownership. As a result, regulators expect these industries to implement stronger controls around client identification, risk assessment, record keeping, and suspicious activity reporting.
For many firms in these sectors, AML compliance has traditionally been managed through manual procedures and administrative processes. Client identification might occur through scanned documents, email exchanges, or basic identity verification checks. Records may be stored across multiple systems such as document management platforms, CRM tools, property management systems, and accounting software.
Under AUSTRAC supervision, these fragmented approaches become difficult to defend. Regulators expect organisations to demonstrate consistent client due diligence, reliable data retention, and clear audit trails across their systems.
This shift means that AML compliance will increasingly depend on the technology environment supporting business operations, rather than policy documents alone. Systems must be capable of capturing accurate information, maintaining records for required retention periods, and producing evidence if regulators request it.
For real estate, accounting and legal firms preparing for Tranche 2, the key challenge is ensuring that their operational systems align with the governance expectations that AUSTRAC will apply from July 2026 onwards.
Why Technology Systems Will Determine Compliance Success
While AML policies often focus on procedures and governance, compliance outcomes are ultimately determined by how effectively technology systems support those procedures in practice.
Modern professional services firms rely heavily on digital systems for everyday operations. Client onboarding platforms capture identity information. CRM systems store contact records and engagement details. Document management platforms retain contracts and verification documents. Financial systems track transactions and trust account activity.
Each of these systems plays a role in the client due diligence lifecycle.
If these systems operate independently without consistent governance, organisations can quickly lose visibility over where client information resides and whether it meets compliance standards. For example, identity verification might occur through one platform, while supporting documentation is stored in another system and transaction records are held elsewhere.
This fragmentation creates several risks. Data may be incomplete, inconsistently stored, or difficult to retrieve during an investigation. Access controls may vary between platforms and gaps creates opportunities for misuse. Retention policies may not be enforced consistently.
From a regulatory perspective, these weaknesses make it difficult for organisations to demonstrate that client due diligence processes are operating as intended.
An independent IT audit examines whether these systems collectively support compliance objectives. It evaluates how client data flows through the organisation, whether controls are applied consistently, if data integrity is maintained and whether records can be retrieved reliably when required.
By identifying gaps in system configuration, integration, and governance, organisations can address potential weaknesses before regulatory scrutiny increases.
For professional services firms approaching the 2026 AUSTRAC compliance deadline, the strength of their technology controls may ultimately determine whether their AML frameworks stand up to external review.
Digital Client Due Diligence: Where Many Firms Are Exposed
Client due diligence sits at the core of AML compliance. Organisations must be able to identify clients, verify their identity, assess risk, and retain evidence that these steps have been performed appropriately.
For real estate, accounting and legal firms, this process increasingly occurs through digital onboarding systems and identity verification platforms. While these technologies have improved efficiency, they have also introduced new governance challenges.
Many organisations implement digital verification tools quickly to streamline client onboarding, but over time the surrounding controls can become inconsistent. Identity checks may occur through different platforms depending on the service line or office location. Supporting documentation may be uploaded into separate document systems or stored in email threads and cause privacy compliance issues. Risk assessments may be recorded in spreadsheets or CRM notes rather than within structured workflows.
This fragmented approach makes it difficult to demonstrate that due diligence has been applied consistently across all clients and transactions.
Regulators expect firms to be able to show clear evidence of the verification process, including the method used, the data collected, and the decision-making process behind risk classifications. If this information is scattered across multiple systems, responding to an AUSTRAC review becomes far more complex.
An IT audit reviews the systems supporting digital client onboarding to determine whether verification processes are standardised, traceable, and governed effectively. It examines how identity verification tools integrate with CRM systems, how supporting documents are stored, and whether audit trails exist for client risk assessments.
For organisations preparing for Tranche 2, strengthening these digital due diligence processes is essential. Without reliable system controls, even well-written compliance policies may struggle to withstand regulatory scrutiny.
Data Retention and Evidence Requirements Under AUSTRAC Oversight
AML compliance does not end with client verification. Organisations must also ensure that records relating to client identification, transactions, and due diligence decisions are retained, maintain integrity and are accessible for regulatory review.
Under AUSTRAC expectations, firms may need to demonstrate how client information was collected, how risk was assessed, and how decisions were documented. This means that records must be accurate, secure, and retrievable for the required retention period.
In many professional services environments, however, client information is stored across multiple platforms. Document management systems may contain contracts and identification records. CRM systems may hold engagement information. Financial systems track transactions. Additional information may exist in email archives or shared drives.
Without clear governance, this distributed environment creates challenges. Documents may be duplicated across systems, stored without consistent naming conventions, or retained indefinitely without structured policies. Access controls may vary between platforms, increasing the risk of unauthorised access or accidental deletion.
From a regulatory standpoint, these weaknesses create uncertainty about whether the organisation can produce reliable evidence when required.
An IT audit examines how client data is stored, managed, and retained across the organisation. It evaluates whether retention policies are applied consistently, whether document repositories provide reliable audit trails, and whether records can be retrieved efficiently if regulators request them.
For real estate, accounting and legal firms entering the AML regulatory framework, the ability to demonstrate structured, defensible record management will become a key component of compliance. Technology systems must support this requirement by ensuring that client data remains organised, protected, and accessible throughout its lifecycle.
How an Independent IT Audit Identifies Compliance Blind Spots
Preparing for AML/CTF Tranche 2 requires organisations to move beyond assumptions about compliance and develop evidence-based confidence in their systems and controls.
Internal IT teams often manage the technology environment effectively, but they may not always have the capacity or independence to evaluate whether systems align with regulatory expectations. Compliance responsibilities are frequently shared across departments, which can make it difficult to gain a complete view of how systems support due diligence and record management.
This is where an independent IT audit provides additional value.
Rather than focusing solely on policy documentation, the audit examines how technology controls operate in practice. It assesses system configurations, access controls, integration between platforms, and the reliability of audit trails. The objective is to determine whether the organisation can demonstrate consistent compliance across its operational systems.
For professional services firms preparing for AUSTRAC oversight, this review often reveals practical issues that may not be visible internally. These can include gaps in data retention configuration, inconsistent onboarding processes between departments, or limited monitoring capability across multiple platforms.
By identifying these blind spots early, organisations can prioritise remediation efforts before regulatory scrutiny increases.
Beyond Technology conducts independent IT governance and compliance audits that assess the systems supporting AML obligations, including client onboarding platforms, document repositories, and monitoring processes. The outcome is a clear view of control maturity and a practical roadmap for strengthening compliance capability.
For organisations facing the 2026 AML/CTF Tranche 2 deadline, this level of visibility helps leadership move from uncertainty to structured preparedness.
Building Sustainable AML Governance Through Technology Controls
While many organisations initially approach AML compliance as a regulatory requirement, the most effective firms treat it as a long-term governance discipline supported by well-structured technology controls.
Tranche 2 will require firms to demonstrate not only that controls exist, but that they are operating consistently, reviewed regularly, and supported by reliable systems. This means compliance cannot rely solely on manual processes or individual staff knowledge. It must be embedded within the organisation’s technology environment.
Sustainable AML governance begins with clearly defined ownership of systems that support compliance activities. Client onboarding platforms, document management systems, and transaction records must operate within structured governance frameworks where responsibilities, review cycles, and control monitoring are clearly defined.
Technology also plays a key role in ensuring consistency. Standardised onboarding workflows, integrated identity verification processes, and structured data retention policies help reduce the risk of inconsistent due diligence practices across offices, teams, or service lines.
Equally important is the ability to review and improve controls over time. As regulatory expectations evolve and business operations change, organisations must periodically reassess whether their systems still support compliance objectives.
Independent audits contribute to this continuous improvement cycle by providing objective insight into the maturity of existing controls and identifying opportunities for improvement.
Beyond Technology works with professional services firms to establish sustainable IT governance structures that align technology systems with regulatory obligations. Through structured IT audits and governance reviews, organisations gain a clearer understanding of how their systems support compliance and where improvements may be required.
For firms preparing for AUSTRAC oversight in 2026, building this governance capability now ensures that AML compliance becomes a stable and defensible operational process, rather than a reactive response to regulatory pressure.
Final Thoughts
AML/CTF Tranche 2 represents a significant shift for professional services firms that have historically operated outside direct AUSTRAC supervision. For real estate agencies, legal and accounting practices, and other gatekeeper professions, compliance will increasingly depend on how effectively technology systems support client due diligence, record keeping, and governance processes.
Policies and procedures remain important, but regulators ultimately expect organisations to demonstrate that those policies are operating consistently in practice. This requires systems capable of capturing reliable client information, maintaining defensible records, and producing clear evidence when regulators request it.
For many firms, the biggest risk lies not in the absence of compliance frameworks, but in the fragmented technology environments that support day-to-day operations. Disconnected onboarding systems, inconsistent document storage, and unclear data governance can make it difficult to demonstrate compliance even when policies exist.
Independent IT audits help organisations address this challenge by providing objective visibility into how technology controls operate across the business. They identify gaps between compliance expectations and system capability, allowing organisations to strengthen governance before regulatory scrutiny increases.
As the July 2026 AUSTRAC deadline approaches, professional services firms that proactively review their systems will be far better positioned to demonstrate compliance, protect client data, and maintain confidence in their governance frameworks.
FAQs Answered
1. How can real estate, accounting and legal firms prepare their systems for AML/CTF Tranche 2 compliance?
Preparation begins with understanding whether the systems supporting client onboarding, identity verification, and record retention can demonstrate consistent compliance. Many firms implemented digital tools to improve efficiency, but those systems were not always designed with regulatory auditability in mind.
An effective starting point is a structured review of how client information is collected, verified, stored, and retained across the organisation’s technology environment. This includes examining onboarding workflows, identity verification platforms, CRM records, document management systems, and the audit trails generated by those platforms.
Beyond Technology works with professional services firms to assess these environments through independent IT audits. The objective is to identify where controls are working well, where gaps exist, and how systems can be strengthened to support AUSTRAC expectations before the 2026 compliance deadline.
2. What technology systems should be reviewed during an AML compliance audit?
An AML-focused IT audit typically examines the systems involved in the client lifecycle, from initial onboarding through to ongoing record retention.
This often includes digital identity verification platforms, client onboarding portals, CRM systems, document management repositories, trust accounting or financial systems, and any platforms used to capture beneficial ownership or risk assessments.
The audit focuses on how these systems interact and whether they collectively provide reliable evidence of due diligence activities. It also reviews access controls, audit logging, backups, document retention policies, and system integrations that influence how client information flows across the organisation.
Beyond Technology evaluates both the technical configuration and the governance processes surrounding these platforms to ensure they support defensible compliance outcomes.
3. How should organisations manage digital client due diligence records?
Client due diligence records should be stored in a way that ensures they are consistent, secure, and easily retrievable if regulators request evidence.
This typically requires structured document management processes where identity verification results, supporting identification documents, and risk assessments are linked clearly to the relevant client record. Retention policies should also ensure that records remain available for the required regulatory timeframe.
In many organisations, however, due diligence records become fragmented across multiple systems or stored in email archives and shared drives. This makes it difficult to reconstruct the verification process during regulatory reviews.
Beyond Technology helps organisations design data governance approaches that ensure due diligence records are captured systematically and retained within platforms capable of supporting regulatory audit and privacy requirements.
4. Why is data governance critical for AML compliance in professional services firms?
AML compliance relies on the ability to demonstrate that client information is accurate, complete, and consistently managed across systems. Without strong data governance, organisations risk maintaining multiple versions of client records across different platforms.
This fragmentation creates uncertainty around which record is authoritative and whether due diligence processes have been applied consistently. It can also complicate investigations or regulatory inquiries when organisations are unable to locate or reconcile information quickly.
Effective data governance ensures that client information is captured once, managed consistently, and protected by appropriate access controls and retention policies.
Beyond Technology supports organisations in strengthening these governance practices so that compliance obligations are supported by reliable and well-managed data environments.
5. When should organisations engage an independent IT governance advisor for AML readiness?
Independent review is particularly valuable when organisations are preparing for new regulatory oversight or when leadership requires assurance that existing systems are capable of supporting compliance obligations.
Many internal teams are focused on day-to-day operational delivery and may not have the capacity or independence required to evaluate whether technology controls align with regulatory expectations.
Engaging an independent advisor provides objective visibility into the maturity of systems and controls. It allows organisations to identify risks early and prioritise remediation activities before external scrutiny increases.
Beyond Technology provides independent governance assessments designed to help organisations understand their current control maturity and develop practical improvement roadmaps aligned with regulatory expectations.
6. How does Beyond Technology help organisations prepare for AUSTRAC compliance audits?
Beyond Technology specialises in independent IT governance and compliance assessments that help organisations translate regulatory requirements into practical technology controls.
Our audits review the systems supporting client onboarding, identity verification, document retention, monitoring processes, and governance oversight. The objective is to determine whether those systems collectively provide reliable evidence of compliance.
Rather than focusing solely on policy documentation, our approach evaluates how controls operate in real business environments. This allows leadership teams to understand where technology controls are strong, where gaps exist, and what improvements should be prioritised.
For professional services firms preparing for AML/CTF Tranche 2, this independent perspective provides the clarity needed to ensure that compliance frameworks are supported by systems that are defensible, auditable, and aligned with regulatory expectations.
FAQs answered
How can real estate, accounting and legal firms prepare their systems for AML/CTF Tranche 2 compliance?
Preparation begins with understanding whether the systems supporting client onboarding, identity verification, and record retention can demonstrate consistent compliance. Many firms implemented digital tools to improve efficiency, but those systems were not always designed with regulatory auditability in mind. An effective starting point is a structured review of how client information is collected, verified, stored, and retained across the organisation’s technology environment. This includes examining onboarding workflows, identity verification platforms, CRM records, document management systems, and the audit trails generated by those platforms. Beyond Technology works with professional services firms to assess these environments through independent IT audits. The objective is to identify where controls are working well, where gaps exist, and how systems can be strengthened to support AUSTRAC expectations before the 2026 compliance deadline.
What technology systems should be reviewed during an AML compliance audit?
An AML-focused IT audit typically examines the systems involved in the client lifecycle, from initial onboarding through to ongoing record retention. This often includes digital identity verification platforms, client onboarding portals, CRM systems, document management repositories, trust accounting or financial systems, and any platforms used to capture beneficial ownership or risk assessments. The audit focuses on how these systems interact and whether they collectively provide reliable evidence of due diligence activities. It also reviews access controls, audit logging, backups, document retention policies, and system integrations that influence how client information flows across the organisation. Beyond Technology evaluates both the technical configuration and the governance processes surrounding these platforms to ensure they support defensible compliance outcomes.
How should organisations manage digital client due diligence records?
Client due diligence records should be stored in a way that ensures they are consistent, secure, and easily retrievable if regulators request evidence. This typically requires structured document management processes where identity verification results, supporting identification documents, and risk assessments are linked clearly to the relevant client record. Retention policies should also ensure that records remain available for the required regulatory timeframe. In many organisations, however, due diligence records become fragmented across multiple systems or stored in email archives and shared drives. This makes it difficult to reconstruct the verification process during regulatory reviews. Beyond Technology helps organisations design data governance approaches that ensure due diligence records are captured systematically and retained within platforms capable of supporting regulatory audit and privacy requirements.
Why is data governance critical for AML compliance in professional services firms?
AML compliance relies on the ability to demonstrate that client information is accurate, complete, and consistently managed across systems. Without strong data governance, organisations risk maintaining multiple versions of client records across different platforms. This fragmentation creates uncertainty around which record is authoritative and whether due diligence processes have been applied consistently. It can also complicate investigations or regulatory inquiries when organisations are unable to locate or reconcile information quickly. Effective data governance ensures that client information is captured once, managed consistently, and protected by appropriate access controls and retention policies. Beyond Technology supports organisations in strengthening these governance practices so that compliance obligations are supported by reliable and well-managed data environments.
When should organisations engage an independent IT governance advisor for AML readiness?
Independent review is particularly valuable when organisations are preparing for new regulatory oversight or when leadership requires assurance that existing systems are capable of supporting compliance obligations. Many internal teams are focused on day-to-day operational delivery and may not have the capacity or independence required to evaluate whether technology controls align with regulatory expectations. Engaging an independent advisor provides objective visibility into the maturity of systems and controls. It allows organisations to identify risks early and prioritise remediation activities before external scrutiny increases. Beyond Technology provides independent governance assessments designed to help organisations understand their current control maturity and develop practical improvement roadmaps aligned with regulatory expectations.
How does Beyond Technology help organisations prepare for AUSTRAC compliance audits?
Beyond Technology specialises in independent IT governance and compliance assessments that help organisations translate regulatory requirements into practical technology controls. Our audits review the systems supporting client onboarding, identity verification, document retention, monitoring processes, and governance oversight. The objective is to determine whether those systems collectively provide reliable evidence of compliance. Rather than focusing solely on policy documentation, our approach evaluates how controls operate in real business environments. This allows leadership teams to understand where technology controls are strong, where gaps exist, and what improvements should be prioritised. For professional services firms preparing for AML/CTF Tranche 2, this independent perspective provides the clarity needed to ensure that compliance frameworks are supported by systems that are defensible, auditable, and aligned with regulatory expectations.
A 30-minute conversation with a partner is the simplest way to see where your organisation stands. No pitch, no sales process – just a senior view of where you are and where the priorities should sit.
Beyond the Office: Auditing Hybrid Work Security 4.0
Hybrid work is permanent, but much of the security architecture underneath it is still the emergency scaffolding of 2020. An independent audit shows whether your controls have matured with your operating model.
Hybrid Work Is Permanent – Emergency Controls Are Not
Hybrid work is no longer a temporary adjustment. For professional services firms, not-for-profits, and all distributed teams across Australia, it is now embedded into operating models. What has not evolved at the same pace is the technology management formality and security architecture supporting it.
Many organisations are still operating on remote access controls implemented in 2020 or 2022. VPN capacity was expanded quickly. Multi-factor authentication was enabled rapidly. Endpoint controls were applied unevenly. At the time, speed was essential. Today, that same emergency architecture and configuration may expose organisations to unnecessary risk.
Regulators and insurers no longer view remote access as exceptional. Under the Notifiable Data Breaches scheme, organisations are expected to take “reasonable steps” to protect personal information regardless of whether employees are in the office or working from home. The perimeter has shifted, but accountability has not.
Hybrid Work Security 4.0 requires a reassessment. Are remote access configurations still appropriate? Are MFA controls resistant to modern bypass techniques? Are home-office devices and networks governed, monitored, and supported consistently?
An independent IT audit provides clarity. It assesses whether current controls meet contemporary threat realities and regulatory expectations, and whether the organisation can demonstrate a defensible security posture if an incident occurs.
Hybrid work is permanent. Security exceptions from 2022 should not be.
Hybrid Work Security Has Matured — But Controls Haven’t
Most organisations improved remote work security quickly during the initial shift to work-from-home. That urgency was appropriate at the time. The problem is that many of those undocumented emergency measures have now become the default architecture, even though the risk environment has changed significantly.
Hybrid work introduces a permanent expansion of the attack surface. Users connect from home networks, shared spaces, personal devices, and unmanaged routers. SaaS tools and cloud services are accessed from everywhere. Identity becomes the perimeter. Yet many organisations still treat remote access as an add-on to the office environment rather than a core operating model.
The typical pattern we see is control drift. Network control exceptions become broader over time to “make things work.” MFA exceptions are added for legacy systems and never removed. Endpoint standards differ by team or location. Monitoring is strong on-site, but weaker once users move off the corporate network.
These gaps rarely trigger alarms day-to-day. They become visible when an incident occurs, when an audit is requested, or when a business partner asks for evidence of security controls. At that point, organisations often realise they cannot clearly demonstrate that controls are consistent, current, and defensible.
Hybrid Work Security 4.0 is about moving from survival-mode controls to deliberate governance. The starting point is a structured audit that identifies where controls have drifted, what is no longer fit for purpose, and what needs uplift to align with today’s threats and expectations.
“Reasonable Steps” Under the NDB Scheme in a Hybrid World
Under Australia’s Notifiable Data Breaches scheme, organisations are required to take “reasonable steps” to protect personal information from misuse, interference, loss, and unauthorised access. In 2026, that obligation clearly extends beyond the physical office.
Hybrid work has fundamentally changed how and where personal information is accessed. Staff now handle client data from home offices, shared workspaces, and mobile environments. The legal obligation has not changed, but the context in which it must be met has.
Regulators assess reasonableness based on proportionality. What risks were foreseeable? What controls were implemented? Were those controls reviewed and maintained? In a hybrid model, this includes remote access security, identity controls, device hardening, monitoring, and incident response capability.
An organisation cannot argue that a breach occurred on a home network and therefore sits outside its responsibility. If corporate systems are accessed remotely, the organisation must demonstrate that it implemented proportionate safeguards to protect that access.
This is where many 2022-era configurations fall short. Controls may exist, but they were not designed for long-term governance. Documentation is incomplete. Review cycles are informal. Exceptions have accumulated.
An IT audit reframes the discussion. Rather than debating whether controls “should be enough,” it assesses whether they can be demonstrated as reasonable under scrutiny. That distinction matters significantly when incidents become reportable.
VPN Health and Architecture Risks
Virtual Private Networks became the backbone of remote work almost overnight. They provided encrypted tunnels into corporate environments and allowed business continuity during disruption. The issue is not that VPNs were deployed. The issue is that many were never re-architected for sustained hybrid operations and the ever increasing cloud delivery of corporate SaaS applications.
In 2026, regulators and auditors expect remote access to be resilient, segmented, monitored, and governed. Yet we frequently see flat VPN access where users are granted broad network visibility once authenticated. Over time, access permissions expand to reduce friction, creating unnecessary exposure.
VPN health also extends beyond uptime. It includes patch management of VPN appliances, configuration hardening, certificate management, logging capability, and alerting integration. Outdated firmware or poorly configured split tunnelling can introduce vulnerabilities that remain invisible until exploited.
Another overlooked area is user lifecycle management. Are departed employees’ VPN credentials revoked promptly? Are third-party contractors isolated appropriately? Is privileged access segmented from standard user access?
A hybrid security audit assesses remote access architecture as a living control, not a one-off deployment. It reviews configuration baselines, access pathways, monitoring coverage, and alignment with current risk tolerance. The goal is not to eliminate remote access, but to ensure it is proportionate, controlled, and defensible under scrutiny.
MFA Bypass and Identity-Based Vulnerabilities
Multi-factor authentication is widely implemented across Australian organisations, and rightly so. It remains one of the most effective controls against credential compromise. However, the presence of MFA does not automatically equal strong identity security.
In hybrid environments, identity is the perimeter. If attackers compromise user credentials and successfully bypass MFA, they often gain the same level of access as legitimate staff. This makes configuration discipline critical.
Common weaknesses include legacy systems that do not enforce MFA, service accounts with elevated privileges and no secondary authentication, and conditional access policies that contain broad exclusions for “trusted” IP ranges or specific user groups. Over time, these exceptions accumulate to reduce friction, but they materially weaken the control environment.
Another risk area is MFA fatigue and push-based authentication abuse. Users repeatedly prompted for approval may inadvertently authorise malicious access attempts. Without monitoring and anomaly detection, these behaviours go unnoticed.
An audit does not simply confirm that MFA exists. It evaluates enforcement consistency, exception management, privilege alignment, phishing resistance, and logging capability. It asks whether identity controls reflect current threat models and whether governance processes exist to review and tighten them over time.
Hybrid Work Security 4.0 recognises that identity controls must evolve continuously. What was adequate in 2022 now falls short of 2026 expectations, particularly when assessed against regulatory scrutiny or cyber insurance requirements.
Home Office Hardware and Endpoint Governance
Hybrid work blurred the boundary between corporate infrastructure and personal environments. In many organisations, laptops were issued quickly, Bring Your Own Device policies were relaxed, and home networks became an assumed extension of the office. The governance challenge is that these environments are rarely standardised or consistently monitored.
From a regulatory perspective, the question is simple: can the organisation demonstrate that devices accessing sensitive data are appropriately secured?
Endpoint governance includes configuration baselines, application control, privilege management, encryption enforcement, patching discipline, remote wipe capability, and monitoring coverage. In practice, we often find gaps. Devices may be encrypted but not centrally monitored. Patch cycles may differ between office-based and remote users. Lost or stolen devices may not be remotely disabled. Personal devices may access corporate SaaS platforms without formal approval.
Home routers and Wi-Fi security introduce further complexity. While organisations cannot control every household network, they can define minimum standards for remote access, enforce secure connection policies, and ensure traffic is routed through monitored channels where appropriate.
An IT audit evaluates whether endpoint controls are documented, enforced, and reviewed. It assesses whether asset registers reflect reality, whether security agents are consistently deployed, and whether monitoring extends beyond the corporate LAN.
In 2026, hybrid governance is not about trusting employees to “do the right thing.” It is about implementing proportionate, evidence-based controls that can withstand external scrutiny.
Incident Readiness in a Distributed Environment
Hybrid work complicates incident response. When systems were centralised, containment was often straightforward. Devices were on-site, networks were segmented within a known perimeter, and response teams could physically intervene if required. In a distributed model, that simplicity no longer exists.
Incidents may begin on a home device, traverse a VPN, or originate from compromised credentials in a SaaS platform. Log data is dispersed across endpoints, cloud services, identity providers, and remote access infrastructure. Without centralised visibility, investigation becomes slow and incomplete, not to mention the recovery complexity when end-point devices are spaced around the country as many experience with the crowdstrike outage back in 2024.
From a Notifiable Data Breach perspective, this delay matters. Organisations are expected to assess whether serious harm is likely and notify the regulator and affected individuals promptly. If logs are missing, monitoring is inconsistent, or endpoint telemetry is limited, that assessment becomes guesswork rather than evidence-based analysis.
A hybrid security audit reviews whether monitoring extends across remote users, whether logs are retained and centrally aggregated, and whether investigation playbooks account for distributed endpoints. It also evaluates tabletop exercises and recovery testing in hybrid scenarios.
The objective is not to eliminate incidents. It is to understand the implications of risk and ensure that when incidents occur, the organisation can respond decisively, contain the impact, and demonstrate control effectiveness.
Incident readiness is the practical test of hybrid governance maturity. Controls that appear strong in documentation often reveal weaknesses when a response is simulated.
What a Hybrid Work Security Audit Should Cover
A hybrid work security audit must go beyond checklist validation. It should assess whether remote access, identity, endpoint, and monitoring controls operate cohesively and proportionately to the organisation’s risk profile.
At a minimum, a structured audit should review:
• Remote access architecture and configuration • MFA enforcement consistency, phishing resistance and exception management • Privileged access segmentation and lifecycle controls • Endpoint configuration baselines and patch compliance • Device encryption and remote wipe capability • Centralised logging and monitoring coverage • Incident response readiness in distributed scenarios • Alignment with the Notifiable Data Breaches scheme and privacy obligations
However, control presence alone is not sufficient. The audit must also evaluate governance maturity. Are review cycles documented? Is ownership clearly assigned? Are exceptions formally approved and revisited? Can leadership demonstrate that controls are regularly assessed and improved?
For any organisation including professional services firms and not-for-profits with distributed teams, the reputational risk of a breach is significant. Clients, donors, and regulators expect visible diligence. Hybrid governance is no longer optional or temporary. It is core operational infrastructure.
An effective audit provides clarity. It identifies where 2022-era configurations have drifted, where documentation is incomplete, and where controls need uplift to meet 2026 expectations.
The outcome is not fear-based. It is a prioritised roadmap aligned to business risk tolerance.
How Beyond Technology Approaches Hybrid Work Security Audits
Beyond Technology approaches hybrid work security through the lens of governance, not just configuration. Our objective is to provide independent, evidence-based visibility into whether controls are proportionate, defensible, and aligned to regulatory expectations.
We begin by understanding the organisation’s operating model and recent growth trajectory. How many staff are remote? What systems hold sensitive information? Which services are cloud-based? What regulatory obligations apply? This context shapes the audit scope and ensures recommendations are risk-aligned rather than generic.
Our assessment examines architecture, configuration, and governance processes. We review VPN health and segmentation, MFA enforcement and exceptions, privileged access discipline, endpoint configuration baselines, monitoring capability, and incident response readiness. Where appropriate, we test controls and validate documentation against operational reality.
Importantly, we do not sell any technology or a specific platform. Our advice is technology-agnostic and independent. If controls are effective, we confirm that. If they are misaligned, we identify proportionate remediation pathways without driving unnecessary spend.
The outcome is a clear maturity assessment and prioritised uplift plan. Leadership gains visibility over whether hybrid security measures satisfy the “reasonable steps” expectation under the Notifiable Data Breaches scheme and broader governance obligations.
Hybrid Work Security 4.0 is about moving from reactive patchwork controls to sustainable operational resilience.
Final Thoughts
Broad based hybrid working is no longer a temporary arrangement. It is a structural shift in how Australian organisations operate. Clients expect flexibility. Staff expect mobility. Boards expect resilience. Regulators expect demonstrable diligence.
The controls deployed in 2022 achieved continuity under pressure. In 2026, that is no longer enough. Expectations have evolved. Threat actors are more sophisticated. Privacy obligations are clearer. Cyber insurance requirements are tighter. What was previously considered reasonable may now be seen as insufficient.
The critical question for leadership is not whether hybrid controls exist. It is whether they are proportionate, reviewed, consistently enforced, and defensible under scrutiny.
An independent hybrid work security audit provides that clarity. It identifies configuration drift, unmanaged exceptions, monitoring blind spots, and governance gaps. It transforms assumptions into evidence and reactive fixes into structured improvement.
For professional services firms and not-for-profits with distributed teams, reputational impact often exceeds direct financial loss. Trust, once eroded, is difficult to rebuild. Demonstrable control maturity is therefore both a compliance requirement and a strategic safeguard.
If your hybrid security architecture was initially designed under emergency conditions and has not been formally reviewed since, it is time to reassess.
Beyond Technology’s IT Audit framework helps organisations evaluate remote access, identity, endpoint, and incident readiness controls against current regulatory and operational expectations.
Hybrid work is permanent. Security governance must be equally deliberate.
FAQs Answered
1. How can organisations assess whether their hybrid work security controls meet regulatory expectations?
The only reliable way to assess hybrid security maturity is through a structured, independent review of remote access, identity, endpoint, and monitoring controls. Many organisations assume their controls are adequate because they were implemented during the initial shift to remote work. An audit tests whether those controls are consistently enforced, proportionate to risk, and defensible under the Notifiable Data Breaches scheme. Beyond Technology provides independent hybrid security audits that convert assumptions into evidence and identify practical uplift priorities.
2. What should a hybrid work security audit include?
A comprehensive audit should review remote access configuration and segmentation, MFA enforcement and exception management, privileged access controls, endpoint hardening standards, remote wipe capability, patch compliance, and centralised monitoring coverage. It should also evaluate governance processes, including review cycles and ownership. Beyond Technology assesses both technical implementation and governance maturity to ensure hybrid controls are sustainable and audit-ready.
3. Are 2022-era remote work controls still sufficient in 2026?
In many cases, no. Controls deployed quickly during emergency remote transitions often lack formal review, documentation discipline, and structured governance. Over time, exceptions accumulate and risk tolerance shifts. Regulatory scrutiny has also increased. Beyond Technology helps organisations reassess legacy hybrid configurations against current threat models and compliance expectations.
4. How does hybrid work impact obligations under the Notifiable Data Breaches scheme?
Hybrid work expands the environments where personal information is accessed and processed. Organisations remain responsible for taking reasonable steps to protect that data, regardless of whether staff are working from home or the office. A hybrid security audit evaluates whether controls surrounding remote access and endpoint management can withstand regulatory scrutiny if a breach occurs.
5. When should organisations engage an independent hybrid security advisor?
Independent review is particularly valuable when internal teams lack capacity, when controls have not been formally reviewed in several years, or when leadership requires assurance before cyber insurance renewal or regulatory reporting. Beyond Technology provides objective assessments without promoting specific platforms, ensuring recommendations are proportionate and risk-aligned.
6. How does Beyond Technology strengthen hybrid work governance?
Beyond Technology conducts structured IT audits that assess remote access architecture, identity controls, endpoint standards, monitoring coverage, and incident readiness. We provide clear maturity ratings and prioritised remediation roadmaps aligned to regulatory and operational risk. Our approach helps leadership demonstrate that hybrid security controls are deliberate, reviewed, and defensible.
{ “@context”: “https://schema.org”, “@type”: “FAQPage”, “mainEntity”: [ { “@type”: “Question”, “name”: “How can organisations assess whether their hybrid work security controls meet regulatory expectations?”, “acceptedAnswer”: { “@type”: “Answer”, “text”: “The only reliable way to assess hybrid security maturity is through a structured, independent review of remote access, identity, endpoint, and monitoring controls. Many organisations assume their controls are adequate because they were implemented during the initial shift to remote work. An audit tests whether those controls are consistently enforced, proportionate to risk, and defensible under the Notifiable Data Breaches scheme. Beyond Technology provides independent hybrid security audits that convert assumptions into evidence and identify practical uplift priorities.” } }, { “@type”: “Question”, “name”: “What should a hybrid work security audit include?”, “acceptedAnswer”: { “@type”: “Answer”, “text”: “A comprehensive audit should review remote access configuration and segmentation, MFA enforcement and exception management, privileged access controls, endpoint hardening standards, remote wipe capability, patch compliance, and centralised monitoring coverage. It should also evaluate governance processes, including review cycles and ownership. Beyond Technology assesses both technical implementation and governance maturity to ensure hybrid controls are sustainable and audit-ready.” } }, { “@type”: “Question”, “name”: “Are 2022-era remote work controls still sufficient in 2026?”, “acceptedAnswer”: { “@type”: “Answer”, “text”: “In many cases, no. Controls deployed quickly during emergency remote transitions often lack formal review, documentation discipline, and structured governance. Over time, exceptions accumulate and risk tolerance shifts. Regulatory scrutiny has also increased. Beyond Technology helps organisations reassess legacy hybrid configurations against current threat models and compliance expectations.” } }, { “@type”: “Question”, “name”: “How does hybrid work impact obligations under the Notifiable Data Breaches scheme?”, “acceptedAnswer”: { “@type”: “Answer”, “text”: “Hybrid work expands the environments where personal information is accessed and processed. Organisations remain responsible for taking reasonable steps to protect that data, regardless of whether staff are working from home or the office. A hybrid security audit evaluates whether controls surrounding remote access and endpoint management can withstand regulatory scrutiny if a breach occurs.” } }, { “@type”: “Question”, “name”: “When should organisations engage an independent hybrid security advisor?”, “acceptedAnswer”: { “@type”: “Answer”, “text”: “Independent review is particularly valuable when internal teams lack capacity, when controls have not been formally reviewed in several years, or when leadership requires assurance before cyber insurance renewal or regulatory reporting. Beyond Technology provides objective assessments without promoting specific platforms, ensuring recommendations are proportionate and risk-aligned.” } }, { “@type”: “Question”, “name”: “How does Beyond Technology strengthen hybrid work governance?”, “acceptedAnswer”: { “@type”: “Answer”, “text”: “Beyond Technology conducts structured IT audits that assess remote access architecture, identity controls, endpoint standards, monitoring coverage, and incident readiness. We provide clear maturity ratings and prioritised remediation roadmaps aligned to regulatory and operational risk. Our approach helps leadership demonstrate that hybrid security controls are deliberate, reviewed, and defensible.” } } ] }
A 30-minute conversation with a partner is the simplest way to see where your organisation stands. No pitch, no sales process – just a senior view of where you are and where the priorities should sit.
The 2026 Australian Privacy Act Reforms: An IT Audit Survival Guide
The 2026 Privacy Act reforms turn privacy from a legal obligation into a systems problem. Regulators now expect organisations to demonstrate privacy in their technology, not just in their policies.
The 2026 Australian Privacy Act reforms will mark a fundamental shift in how privacy compliance is assessed and enforced. For many organisations, privacy has historically been treated as a legal or policy-led obligation. That approach is no longer sufficient. Regulators now expect organisations to demonstrate that privacy protections are embedded into the way technology systems are designed, operated, and monitored.
Central to this shift will be the introduction of the “fair and reasonable” test, which moves privacy compliance away from intent and documentation and toward measurable outcomes. It is no longer enough to say reasonable steps were taken. Organisations must be able to prove that their technical controls, data handling practices, and risk decisions align with what is objectively fair and reasonable in their specific operating context.
Mandatory Privacy Impact Assessments (PIAs) further reinforce this expectation. PIAs are no longer theoretical exercises. They directly influence system architecture, vendor selection, data flows, and security controls. When conducted poorly or treated as a tick-box exercise, they expose organisations to regulatory scrutiny rather than reducing risk.
For mid-market Australian firms, this creates a practical challenge. Legal advice explains the obligation, but it does not implement controls or generate audit-ready evidence. This is where IT audits can play a critical role. They translate legislative requirements into technical reality, ensuring organisations can demonstrate compliance through systems, controls, and evidence rather than assumptions.
Summary Table
Reform Area
New Expectation
IT Control Impact
Audit Evidence Required
Fair and Reasonable Test
Privacy decisions must be objectively defensible
Access controls, logging, data minimisation, monitoring
Control design, configurations, risk decisions
Mandatory PIAs
Privacy risk assessed before system changes
Architecture reviews, vendor assessments, data flow mapping
PIA records, approvals, mitigation actions
Enforcement Focus
Outcomes over intent
Measurable security and privacy controls
Technical evidence and operational artefacts
Accountability
Ongoing compliance, not one-off reviews
Continuous monitoring and governance
Audit trails and review records
What Changed in the 2026 Privacy Act Reforms (and Why IT Is on the Hook)
The 2026 reforms to the Australian Privacy Act will represent a deliberate move away from principle-based compliance toward enforceable, outcome-driven expectations. While privacy obligations have existed for decades, regulators are now far more explicit about how those obligations are assessed and enforced.
One of the most significant changes is the emphasis on whether an organisation’s handling of personal information is fair and reasonable in the circumstances. This test requires regulators to consider the nature of the data, the way it is used, the risks involved, and the safeguards in place. Importantly, it also requires organisations to justify their decisions with evidence. This shifts accountability from written policies to operational controls.
The reforms also strengthen requirements around Privacy Impact Assessments, particularly where systems, technologies, or business processes are likely to create heightened privacy risk. PIAs are no longer optional best practice. They are an expected governance mechanism that informs design decisions before risk is introduced.
For IT teams, this represents a clear change in responsibility. Privacy compliance is no longer satisfied by legal sign-off or documented intent. Regulators increasingly examine how systems are configured, how access is controlled, how data is monitored, and how risks are mitigated in practice. Where controls are weak, inconsistent, or undocumented, organisations struggle to demonstrate that their approach is reasonable.
Mid-market organisations often feel this pressure most acutely. They are large enough to attract regulatory attention, but frequently lack the structured audit discipline of larger enterprises. In this environment, IT audits become a critical tool. They provide independent assessment of whether technical controls align with legal expectations and whether evidence exists to support compliance claims.
The “Fair and Reasonable” Test — From Legal Language to Technical Reality
The introduction of the “fair and reasonable” test is one of the most consequential elements of the 2026 Privacy Act reforms. While the wording may appear subjective, in practice it creates a clear expectation: organisations must be able to demonstrate that their handling of personal information is proportionate, justified, and supported by appropriate safeguards.
Regulators do not assess fairness based on intent alone. They examine the technical and operational measures in place to protect personal information. This includes how access is controlled, how data is monitored, how long information is retained, and how risks are identified and mitigated. In effect, the “fair and reasonable” test becomes a control assessment, not a policy review.
For IT teams, this shifts the compliance burden squarely into the technical domain. Systems that collect or process personal information must be designed with privacy protections embedded by default. Excessive access privileges, poor logging, weak monitoring, or unclear data flows are difficult to justify as reasonable in a modern threat environment.
Mid-market organisations often struggle here because controls evolve organically rather than through deliberate design. Over time, exceptions accumulate, monitoring becomes inconsistent, and documentation falls behind reality. During regulatory review, these gaps are interpreted as a failure to take reasonable steps, regardless of original intent. As more AI systems are considered for deployment it becomes a critical step to assess the privacy controls so that you can demonstrate compliance if an unexpected event attracts regulatory interest.
An IT audit provides the structure needed to assess fairness objectively. By examining system configurations, access controls, monitoring capability, and data handling practices, audits translate abstract legal language into measurable technical outcomes. They also create the evidence trail regulators expect to see.
The practical question organisations should ask is not whether their privacy approach sounds reasonable, but whether it can be demonstrated as reasonable through evidence. Where that evidence is weak or incomplete, risk exposure increases significantly.
Mandatory Privacy Impact Assessments and Their Impact on IT Infrastructure
Mandatory Privacy Impact Assessments (PIAs) are a central pillar of the 2026 Privacy Act reforms, particularly where new systems, technologies, or processes are likely to introduce heightened privacy risk. While PIAs have existed for some time, the reforms elevate them from recommended practice to an expected governance control that directly influences technology decisions.
In practice, many organisations treat PIAs as documentation exercises completed after systems are selected or implemented. This approach undermines their purpose. A PIA conducted too late cannot meaningfully influence architecture, vendor selection, or data flow design. Worse, it creates a record of known risk that has already been accepted without mitigation.
Under the reformed framework, PIAs are intended to inform design before risk is introduced. This has direct implications for IT infrastructure. Cloud platforms, SaaS applications, system integrations, identity models, and data storage locations all fall within scope. Decisions about where data is stored, who can access it, how it is monitored, and how long it is retained must be defensible within the PIA.
From an audit perspective, PIAs are not assessed in isolation. Regulators and auditors look for alignment between PIA outcomes and actual system implementation. Where a PIA identifies a risk, they expect to see corresponding technical controls or documented risk acceptance. Gaps between assessment and execution are viewed as governance failures.
Mid-market organisations frequently struggle with this alignment. PIAs are owned by risk or legal teams, while implementation sits with IT. Without a structured handover and verification process, mitigation actions are incomplete or inconsistently applied.
IT audits or advisory help close this gap. Audits verify that PIA findings are reflected in system configuration, access controls, logging, and monitoring, while advisory services can provide guidance on how to undertake PIA’s effectively and ensure that the process occurs as required. They also ensure PIAs remain current as systems evolve, integrations change, or data usage expands.
The key question is whether PIAs are actually being performed and are actively shaping technology outcomes, or merely documenting decisions after the fact. In 2026, only the former will stand up to scrutiny.
What Privacy Auditors Will Now Expect to See
Under the 2026 Privacy Act reforms, privacy audits are increasingly evidence-driven. Auditors are no longer satisfied with policy statements or high-level assurances. They expect to see how privacy obligations are translated into operational controls and how those controls are maintained over time.
In practice, this means auditors focus on how personal information is handled within systems, not how compliance is described on paper. They look for evidence that access is restricted appropriately, data flows are understood, risks are monitored, and decisions are documented. Where controls exist but cannot be demonstrated, they are treated as ineffective.
Common audit artefacts now include system access reviews, logging and monitoring records, configuration evidence, and documentation showing how Privacy Impact Assessment findings were implemented. Auditors also test whether controls operate consistently across environments, including cloud platforms, SaaS tools, and third-party integrations.
Mid-market organisations often encounter issues where controls are informal or inconsistently applied. Examples include excessive access privileges, incomplete logging, undocumented system changes, or PIAs that identify risks without corresponding mitigation evidence. These gaps are typically interpreted as failures to take reasonable steps, even when no incident has occurred.
Another area of focus is governance continuity. Auditors increasingly expect to see review cycles, ownership, and evidence that controls are reassessed as systems and risks change. One-off remediation efforts or outdated evidence are no longer sufficient.
The practical reality is that privacy audits now resemble technical control assessments, not legal compliance checks. Organisations that prepare accordingly reduce audit friction, shorten remediation cycles, and significantly lower regulatory risk.
Using IT Audits and Advisory to Bridge Legal Compliance and Technical Execution
One of the most common challenges organisations will face under the 2026 Privacy Act reforms is the disconnect between legal interpretation and technical implementation. Legal advice defines obligations, but it does not configure systems, restrict access, or generate operational evidence. Without a structured mechanism to translate requirements into controls, compliance remains theoretical. Organisations should consider getting independent IT advice on how to prepare for these changes.
IT audits also play a critical role in closing this gap. They provide an independent, practical assessment of whether technical controls align with privacy obligations and whether those controls operate consistently across the environment. Rather than focusing on policy wording, IT audits examine how data is actually handled within systems.
This includes assessing access controls, logging and monitoring capability, data retention practices, third-party integrations, thir-party technical assessments, and the technical implementation of Privacy Impact Assessment outcomes. Where gaps exist, audits identify whether the issue is control design, execution, or governance oversight.
For mid-market organisations, this approach is particularly valuable. Internal teams are often close to day-to-day operations and may lack the objectivity or time required to assess controls against evolving regulatory expectations. An independent audit provides clarity on current posture and prioritises remediation based on risk rather than assumption.
Importantly, IT audits also create the evidence trail regulators expect to see. Findings, remediation actions, and review cycles demonstrate that privacy compliance is being actively managed, not addressed only when prompted by an audit or incident.
The practical benefit is confidence. Organisations that use IT audits to bridge legal requirements and technical reality are better positioned to respond to regulatory scrutiny, reduce privacy risk, and support ongoing system change without reintroducing compliance gaps.
How Beyond Technology Supports Privacy Compliance Readiness
Meeting the expectations of the 2026 Privacy Act reforms requires more than awareness of the law. It requires the ability to demonstrate that privacy obligations are embedded into technology design, operational controls, and governance processes. This is where many organisations struggle, particularly in the mid-market, where resources are finite and roles often overlap.
Beyond Technology supports organisations by translating privacy obligations into practical advice and auditable technical controls. Our focus is on helping leadership understand where privacy risk exists today, how it is being managed in practice, and what evidence is available to support compliance claims.
Through our Information Security and Privacy Health Check, we assess how personal information is handled across systems, platforms, and third-party services. This includes reviewing access controls, monitoring and logging capability, data flows, retention practices, and the implementation of Privacy Impact Assessment outcomes. The result is a clear view of current posture against regulatory expectations.
Importantly, Beyond Technology provides independent advice. We are not tied to specific platforms or tools, which allows us to objectively assess control effectiveness and recommend proportionate improvements aligned to the organisation’s operating context.
We also help organisations establish governance mechanisms that sustain compliance over time. This includes review cycles, ownership models, and evidence capture processes that ensure privacy controls remain effective as systems and business needs evolve.
The goal is confidence. Confidence that privacy obligations are understood, controls are operating as intended, and compliance can be demonstrated through evidence rather than explanation.
Final Thoughts: Privacy Compliance Requires Technical Proof, Not Assurances
The 2026 Privacy Act reforms make one thing clear: privacy compliance is no longer judged by policy intent or good faith efforts alone. Organisations must be able to demonstrate that their handling of personal information is fair, reasonable, and supported by appropriate technical controls.
For IT leaders and compliance teams, this represents a shift in mindset. Privacy is now a systems issue, a governance issue, and an audit issue. Mandatory PIAs, outcome-based enforcement, and increased regulatory scrutiny all point to the same conclusion — evidence matters.
Organisations that rely on documentation without validating implementation expose themselves and their directors to unnecessary risk. Those who use IT audits to assess control effectiveness, verify alignment with legal expectations, and generate defensible evidence are far better positioned to adapt.
Beyond Technology helps organisations make this transition. By bridging legal requirements and technical execution, we enable privacy compliance to become a measurable, sustainable part of IT governance rather than a reactive obligation.
FAQs Answered
1. Do organisations need an IT audit to meet the 2026 Australian Privacy Act reforms?
While an IT audit is not explicitly mandated, it has become one of the most effective ways to demonstrate compliance under the 2026 reforms. The “fair and reasonable” test and mandatory Privacy Impact Assessments require evidence that technical controls are operating as intended. An IT audit provides independent validation of control effectiveness and creates the audit trail regulators expect to see.
2. How is the “fair and reasonable” test assessed in practice during a privacy review or audit?
In practice, regulators assess whether privacy risks are proportionately managed through technical and operational controls. This includes access restrictions, monitoring, data minimisation, logging, and governance oversight. Assertions alone are insufficient. Organisations must demonstrate, through evidence, that their systems and processes reasonably protect personal information given the nature and sensitivity of the data involved.
3. When are Privacy Impact Assessments mandatory under the Privacy Act reforms?
Privacy Impact Assessments are expected when new systems, technologies, or changes are likely to introduce heightened privacy risk. This includes new SaaS platforms, AI systems, major system integrations, data analytics initiatives, or changes to how personal information is collected or used. PIAs must inform design decisions and be supported by evidence that identified risks have been addressed or formally accepted.
4. What technical controls do auditors expect to see for privacy compliance in 2026?
Auditors expect to see enforceable access controls, logging and monitoring capability, documented data flows, retention controls, and evidence that PIA outcomes have been implemented. They also assess whether controls operate consistently across environments and are reviewed regularly. Where controls exist but cannot be evidenced, they are typically treated as ineffective.
5. How can mid-market organisations prepare efficiently for Privacy Act compliance audits?
Mid-market organisations benefit from focusing on control effectiveness rather than excessive documentation. An IT audit or health check helps identify priority gaps, validate existing controls, and generate audit-ready evidence. This approach avoids unnecessary remediation and ensures effort is directed toward areas of genuine regulatory and operational risk.
6. When should organisations engage an independent advisor for privacy and IT audit readiness?
Independent advice is valuable when organisations lack visibility over control effectiveness, are preparing for regulatory scrutiny, or are implementing new systems that impact personal information. Beyond Technology supports organisations seeking objective assessment, practical remediation guidance, and confidence that privacy compliance can be demonstrated through evidence rather than explanation.
FAQs answered
Do organisations need an IT audit to meet the 2026 Australian Privacy Act reforms?
While an IT audit is not explicitly mandated, it has become one of the most effective ways to demonstrate compliance under the 2026 reforms. The “fair and reasonable” test and mandatory Privacy Impact Assessments require evidence that technical controls are operating as intended. An IT audit provides independent validation of control effectiveness and creates the audit trail regulators expect to see.
How is the “fair and reasonable” test assessed in practice during a privacy review or audit?
In practice, regulators assess whether privacy risks are proportionately managed through technical and operational controls. This includes access restrictions, monitoring, data minimisation, logging, and governance oversight. Assertions alone are insufficient. Organisations must demonstrate, through evidence, that their systems and processes reasonably protect personal information given the nature and sensitivity of the data involved.
When are Privacy Impact Assessments mandatory under the Privacy Act reforms?
Privacy Impact Assessments are expected when new systems, technologies, or changes are likely to introduce heightened privacy risk. This includes new SaaS platforms, AI systems, major system integrations, data analytics initiatives, or changes to how personal information is collected or used. PIAs must inform design decisions and be supported by evidence that identified risks have been addressed or formally accepted.
What technical controls do auditors expect to see for privacy compliance in 2026?
Auditors expect to see enforceable access controls, logging and monitoring capability, documented data flows, retention controls, and evidence that PIA outcomes have been implemented. They also assess whether controls operate consistently across environments and are reviewed regularly. Where controls exist but cannot be evidenced, they are typically treated as ineffective.
How can mid-market organisations prepare efficiently for Privacy Act compliance audits?
Mid-market organisations benefit from focusing on control effectiveness rather than excessive documentation. An IT audit or health check helps identify priority gaps, validate existing controls, and generate audit-ready evidence. This approach avoids unnecessary remediation and ensures effort is directed toward areas of genuine regulatory and operational risk.
When should organisations engage an independent advisor for privacy and IT audit readiness?
Independent advice is valuable when organisations lack visibility over control effectiveness, are preparing for regulatory scrutiny, or are implementing new systems that impact personal information. Beyond Technology supports organisations seeking objective assessment, practical remediation guidance, and confidence that privacy compliance can be demonstrated through evidence rather than explanation.
A 30-minute conversation with a partner is the simplest way to see where your organisation stands. No pitch, no sales process – just a senior view of where you are and where the priorities should sit.
Strengthening Technical Controls — Managing Privileges, Devices, and Technology Lifecycles
The most damaging weaknesses usually live inside the environment: excessive privileges, unmanaged devices and technology running past its supported life. Managing them is a leadership discipline, not a helpdesk task.
The Hidden Risks Inside Your Technology Environment
Most organisations focus their cyber-security efforts on external threats — attackers, malware, and phishing campaigns. But in practice, the most damaging weaknesses usually can come from inside the environment itself. Excessive administrative privileges, poorly managed devices, and unsupported systems create vulnerabilities that attackers can exploit with minimal effort. These weaknesses don’t make noise. They accumulate quietly, often going unnoticed until an incident exposes them.
Across mid-sized Australian organisations, these internal control failures are some of the most common and the most preventable. The ACSC Essential Eight repeatedly highlights privilege management, device hardening, and patching as foundational cyber controls — yet many organisations treat them as operational housekeeping rather than strategic risk mitigation.
Technical governance is not just an IT concern. It is a core component of organisational resilience and a growing area of regulatory focus. If privileged accounts are not controlled, if devices are unmanaged, or if end-of-life systems remain in production, leaders cannot reasonably claim to have a defensible cyber posture.
This article outlines how organisations can strengthen their internal controls by improving three essential disciplines:
Privilege management — ensuring only the right people have the right access.
Device management — securing every endpoint that touches corporate data.
Lifecycle management — retiring technology before it becomes a liability.
Strengthening these areas is one of the fastest ways to reduce cyber exposure and lift overall governance maturity.
Summary Table
Technical Control Area
Common Failure
Why It Matters
Best Practice Control
Privilege Management
Excessive, or unreviewed or everyday admin access
Compromised accounts can lead to full-environment breach
Enforce least privilege access and review admin rights regularly
Device Management
Unhardened or unmanaged devices; no remote wipe
Expanded attack surface; lost device = data exposure
Implement device hardening, MDM, and configuration standards
Lifecycle Management
Unsupported OS/hardware still in use
Permanent exposure to unpatchable vulnerabilities
Maintain inventory, isolate or replace end-of-life assets
Controlling Privileged Access Before It Becomes a Liability
Excessive administrative access remains one of the most common — and most dangerous — vulnerabilities inside Australian organisations. Privileged accounts have broad-reaching power: they can change configurations, access sensitive data, disable logging, and move laterally through systems with minimal resistance. If these accounts are compromised, the attacker gains the same level of authority. That is why uncontrolled administrative privileges are consistently ranked as a leading cause of severe cyber incidents.
The ACSC Essential Eight highlights privilege restriction as a core mitigation strategy. It is one of the simplest controls to implement, yet often the most neglected. In many organisations, privileges expand organically over time. Someone needs access “temporarily,” another retains admin rights after a role change, and soon half the IT team — and sometimes non-IT staff — hold keys they no longer need.
A mature privilege management approach includes:
Least privilege enforcement — users only receive the access required for their role and use separate everyday accounts from admin accounts.
Role-based access definitions — standardising what each role should and should not have.
Regular privilege reviews — auditing accounts quarterly or at minimum bi-annually.
Monitoring and logging — ensuring privileged actions are tracked and reviewable.
The governance question for leaders is simple: Do we know who has administrative rights today, and can we justify every name on that list? If the answer is uncertain, risk is already present.
Tactical takeaway: Request a full list of users with administrative privileges across your critical systems. Review it with your IT team — and challenge every entitlement that isn’t explicitly required for someone’s role and ensure that everyday accounts are separate from admin accounts.
Controlling privileged access is one of the fastest ways to reduce cyber exposure.
Device Management Standards for a Distributed Workforce
In today’s operating environment, every device that connects to your network or accesses your data represents a potential entry point for an attacker. The shift to hybrid work, remote access, and BYOD has expanded the attack surface beyond traditional perimeter security — yet many organisations still rely on outdated or informal device management practices. Without clear standards, device security becomes inconsistent, dependent on individual configuration habits rather than intentional control.
A mature organisation treats device management as a core security discipline, not a convenience activity. The ACSC Essential Eight specifically highlights the need for application hardening, patching, and operating system configuration as frontline defences. These controls only work when implemented through documented, enforced standards.
A defensible device management framework includes:
Documented configuration and hardening standards for laptops, desktops, mobiles, servers, and virtual machines.
Mandatory patching and update cycles, aligned to risk and business criticality.
Mobile Device Management (MDM) to maintain control of corporate devices, enforce security settings, and manage applications remotely.
Remote wipe capability for all devices containing corporate data — essential not only for security but for demonstrating due diligence.
Visibility of all active endpoints, including those not directly managed by IT.
When device management is inconsistent, attackers exploit the weakest endpoint. A single unpatched laptop or unmanaged personal device connecting to business systems is all it takes to bypass otherwise strong security measures.
Tactical takeaway: Ask your IT manager one simple question: Can we remotely wipe any corporate device if it is lost or stolen? If the answer is no, Mobile Device Management isn’t a future improvement — it’s an immediate priority.
Strong device management is no longer optional. It is a core pillar of organisational resilience.
Lifecycle Management — Retiring Technology Before It Becomes a Threat
Every piece of technology has a lifecycle. Vendors release patches, updates, and security fixes for a period of time — and then support ends. Once a system reaches end-of-life or end-of-support, any newly discovered vulnerability becomes permanent. This is one of the most underestimated risks inside mid-sized organisations: unsupported technology quietly running in production long after its safe lifespan.
Legacy systems don’t always fail loudly. They continue functioning, which creates a dangerous illusion of stability. But behind the scenes, they introduce governance and security risks that cannot be mitigated through configuration or monitoring alone. Without vendor patches, your organisation is relying on hope — not control.
Effective lifecycle management ensures that outdated technology doesn’t become a silent liability. A mature approach includes:
A complete and accurate hardware and software inventory — the foundation of all lifecycle decisions.
Visibility of end-of-life and end-of-support timelines, with automated flagging where possible.
Risk-based prioritisation, isolating unsupported systems from production environments where replacement is delayed.
Decommissioning procedures that safely retire old systems without introducing new vulnerabilities.
Budgeting and procurement alignment, ensuring lifecycle replacement is planned rather than reactive.
Regulators increasingly view lifecycle maturity as evidence of operational resilience. Unsupported systems undermine this, exposing organisations to breaches, failed audits, and unacceptable levels of operational risk.
The governance test is straightforward: Do we know which systems in our environment are already unsupported, or approaching end-of-support in the next 12–24 36 months? If the answer is no, visibility is the first remediation priority.
Tactical takeaway: Request a consolidated inventory listing all hardware and software, highlighting items that are end-of-life or approaching end-of-support. Establish a remediation or replacement plan for every at-risk asset. Proactive lifecycle management is far more cost-effective than responding to incidents caused by outdated technology.
Lifecycle discipline is not just asset management — it is risk management.
Beyond Technology’s Technical Control Uplift Framework
Improving technical controls isn’t simply an IT housekeeping exercise — it is a governance requirement. Most organisations know they should tighten privileged access, standardise device management, and retire unsupported technology. The problem is execution. Controls drift, exceptions accumulate, and visibility erodes over time. What leaders need is not more theory, but a structured model that delivers measurable uplift. That is where Beyond Technology steps in.
Our Technical Control Uplift Framework helps organisations move from ad-hoc practices to a defensible, standards-aligned security posture. We begin with visibility, conducting a structured assessment across three high-risk domains: privileged access, device management, and technology lifecycle. This provides Boards and executives with a clear understanding of their exposure, supported by evidence — not assumptions.
From there, we build the foundational governance elements that many organisations lack:
Documented access control standards aligned to Essential Eight and ISM
Device configuration and hardening standards, tailored to your environment
Mobile Device Management implementation guidance
Lifecycle policies and asset management processes that prevent future drift
Clear ownership models, ensuring controls don’t lose momentum over time
We then support the operationalisation of these controls by working with your IT teams to embed monitoring, review cycles, and reporting mechanisms. This ensures uplift is not a one-off project but a sustainable discipline.
Finally, we provide ongoing assurance, validating that controls remain effective as technology, threats, and business operations evolve.
The result is a measurable uplift in security maturity — one that reduces risk, strengthens compliance posture, and gives leaders confidence that their control environment will withstand both incidents and audit scrutiny.
Final Thoughts: Control Maturity Is a Leadership Discipline
Privilege management, device security, and lifecycle governance are not technical housekeeping tasks — they are core components of organisational resilience. When these controls weaken, vulnerabilities accumulate silently. Excessive admin access, unmanaged devices, and unsupported systems all increase cyber exposure and reduce a leader’s ability to demonstrate due diligence. These gaps become visible the moment an incident occurs or an auditor starts asking questions.
The organisations that perform best are those that treat technical control maturity as a continuous discipline, not a reactive clean-up. They know who has elevated access. They can secure or wipe any device immediately. They retire technology before it becomes unpatchable. They have visibility, structure, and accountability.
Beyond Technology helps organisations build this discipline. We turn informal practices into documented standards, replace assumptions with measurable controls, and support leaders in building a security posture that is defensible and aligned to the Essential Eight.
Good governance is proven through consistent action — and technical controls are where that action matters most.
FAQs Answered
1. Why is privileged access control considered a high-risk area for cyber security?
Privileged accounts can make system-wide changes, access sensitive data, and bypass many security controls. If compromised, they give an attacker complete freedom inside your environment and the ability to install back doors for future system compromise. Excessive or unmonitored admin access is one of the most common root causes of major breaches. Restricting and regularly reviewing privileged access is one of the fastest ways to reduce cyber risk and improve governance maturity.
2. What should a device management standard include for modern organisations?
A device management standard should define secure configuration requirements, patching expectations, approved applications, encryption settings, and monitoring controls. It should also mandate Mobile Device Management (MDM) for enforcing policies and enabling remote wipe. In hybrid work environments, device standards ensure consistent hardening and reduce the attack surface across laptops, mobiles, and other endpoints accessing corporate data.
3. How often should privileged access rights be reviewed?
Privileged access should be reviewed at least quarterly — or immediately following role changes, restructuring, or system migrations. Regular audits ensure privileges remain aligned to actual responsibilities and help detect excessive access before it becomes a risk. A structured, documented review cycle is essential for demonstrating due diligence and meeting best-practice expectations outlined in the ACSC Essential Eight.
4. What are the risks of running end-of-life or unsupported software and hardware?
End-of-life systems no longer receive security patches, meaning any new vulnerability becomes permanent. These assets create unfixable weaknesses that attackers can exploit easily to access sensitive data or move latterly to compromise other systems. They also introduce compliance, audit, and operational risks. Unsupported systems should be isolated or decommissioned promptly, as they undermine the organisation’s ability to maintain a defensible cyber-security posture.
5. Which frameworks guide best practice for privilege, device, and lifecycle management in Australia?
The ACSC Essential Eight provides clear guidance on restricting privileges, hardening devices, and maintaining patching routines. The ACSC Information Security Manual (ISM) outlines detailed control requirements. These frameworks help organisations implement technical governance that is measurable, repeatable, and aligned to regulatory expectations. Many organisations use them as the benchmark for cyber maturity uplift.
6. How does Beyond Technology help organisations uplift their technical controls?
Beyond Technology conducts structured assessments to identify gaps in privilege management, device hardening, and lifecycle governance. We develop standards, uplift technical controls, implement MDMdevice management processes, and create remediation roadmaps aligned to Essential Eight and ISM guidance. Our goal is to replace ad-hoc practices with consistent, defensible controls that reduce risk and strengthen the organisation’s overall governance posture.
FAQs answered
Why is privileged access control considered a high-risk area for cyber security?
Privileged accounts can make system-wide changes, access sensitive data, and bypass many security controls. If compromised, they give an attacker complete freedom inside the environment and the ability to install back doors for future system compromise. Excessive or unmonitored admin access is one of the most common root causes of major breaches. Restricting and regularly reviewing privileged access is one of the fastest ways to reduce cyber risk and improve governance maturity.
What should a device management standard include for modern organisations?
A device management standard should define secure configuration requirements, patching expectations, approved applications, encryption settings, and monitoring controls. It should also mandate Mobile Device Management (MDM) for enforcing policies and enabling remote wipe. In hybrid work environments, device standards ensure consistent hardening and reduce the attack surface across laptops, mobiles, and other endpoints accessing corporate data.
How often should privileged access rights be reviewed?
Privileged access should be reviewed at least quarterly, or immediately following role changes, restructuring, or system migrations. Regular audits ensure privileges remain aligned to actual responsibilities and help detect excessive access before it becomes a risk. A structured, documented review cycle is essential for demonstrating due diligence and meeting best-practice expectations outlined in the ACSC Essential Eight.
What are the risks of running end-of-life or unsupported software and hardware?
End-of-life systems no longer receive security patches, meaning any new vulnerability becomes permanent. These assets create unfixable weaknesses that attackers can exploit easily to access sensitive data or move laterally to compromise other systems. They also introduce compliance, audit, and operational risks. Unsupported systems should be isolated or decommissioned promptly, as they undermine the organisation’s ability to maintain a defensible cyber-security posture.
Which frameworks guide best practice for privilege, device, and lifecycle management in Australia?
The ACSC Essential Eight provides clear guidance on restricting privileges, hardening devices, and maintaining patching routines. The ACSC Information Security Manual (ISM) outlines detailed control requirements. These frameworks help organisations implement technical governance that is measurable, repeatable, and aligned to regulatory expectations. Many organisations use them as the benchmark for cyber maturity uplift.
How does Beyond Technology help organisations uplift their technical controls?
Beyond Technology conducts structured assessments to identify gaps in privilege management, device hardening, and lifecycle governance. We develop standards, uplift technical controls, implement MDM device management processes, and create remediation roadmaps aligned to Essential Eight and ISM guidance. Our goal is to replace ad-hoc practices with consistent, defensible controls that reduce risk and strengthen the organisation’s overall governance posture.
A 30-minute conversation with a partner is the simplest way to see where your organisation stands. No pitch, no sales process – just a senior view of where you are and where the priorities should sit.
Strengthening Operational Resilience — Recovery Readiness and Change Control Discipline
When ransomware, supply chain failure or a bad change takes systems down, two controls decide how fast you recover: backup capability you have actually tested, and change discipline you actually follow.
Why Operational Controls Fail When They Matter Most
When organisations suffer major outages — whether caused by ransomware, system or digital supply chain failure, or a poorly executed change — two operational controls determine how quickly they recover: recovery readiness and change management discipline. These controls sit at the heart of operational resilience, yet in many mid-sized Australian organisations they remain inconsistent, untested, or undocumented.
The uncomfortable truth is that many businesses have backups or redundancy they cannot reliably restore from. They assume recovery will work, but that assumption is rarely tested. Similarly, many IT teams implement changes without a formal control process, relying instead on experience, goodwill, and institutional memory. When incidents occur, leaders discover the fragility of these assumptions.
The ACSC Essential Eight emphasises regular backups and controlled changes as baseline expectations — not optional enhancements. Regulators and insurers increasingly scrutinise both areas after an incident, asking for evidence that controls were tested and consistently applied. Without that evidence, organisations struggle to demonstrate due diligence.
This article outlines how to uplift operational resilience by strengthening two key areas:
Backup and recovery capability — ensuring data can be restored and systems can be rebuilt.
Change control discipline — ensuring changes are predictable, approved, communicated, and reversible.
Organisations that treat these controls as governance priorities, rather than technical conveniences, experience fewer outages, faster recoveries, and significantly stronger audit outcomes.
Summary Table
Operational Area
Common Failure
Why It Matters
Best Practice Control
Backup & Recovery
Backups and designed redundancy are untested; restores unverified
Restores fail during ransomware or outage; RTO/RPO cannot be met
Documented backup standard, recovery plans + scheduled full restoration testing
Change Control
Informal or inconsistent change processes
Outages, configuration drift, and security vulnerabilities
Formal change management with approvals, impact assessment, and rollback plans
Building Confidence in Backup and Recovery Capability
Backups are often treated as a checkbox — something the IT team assures leadership is happening in the background. But during a ransomware attack or major system outage, the question is not “Do we have backups?” but “Can we actually restore from them?” Many organisations discover too late that their backups are incomplete, corrupted, misconfigured, or simply never tested end to end.
A backup strategy that is not validated through recovery testing is built on assumptions, not evidence. The ACSC Essential Eight classifies regular backups and recovery testing as one of its fundamental mitigation strategies for a reason: the difference between hours of disruption and weeks of downtime often comes down to restoration capability.
Mature backup governance includes:
Documented backup standards defining frequency, scope, retention, and storage location.
Recovery Time Objectives (RTO) and Recovery Point Objectives (RPO) aligned to business needs.
Documented recovery plans
Full restoration testing, not just file-level checks.
Testing of mission-critical workloads, including virtual machines, databases, cloud backups, and SaaS exports.
Documented test results, including duration, success rate, and required improvements.
A schedule for ongoing validation, at least every six months — more frequently for critical systems.
Without these controls, the organisation cannot confidently claim its data is recoverable or that business operations can resume within acceptable timeframes.
The governance test is simple: When was the last time you tested a full system restore, and did it meet the RTO/RPO defined in your business continuity plan? If that answer is unknown or the test hasn’t happened in over six months, the recovery strategy needs immediate uplift.
Tactical takeaway: Ask your IT team for the date and outcome of the last recovery test. If none exists, schedule a full restoration exercise within the next month.
Embedding Formal Change Control and Management Discipline
In many organisations, the most disruptive outages aren’t caused by cyber attacks — they’re caused by well-intentioned but poorly controlled changes. A configuration tweak made during business hours, a patch applied without testing, or a firewall rule adjusted without clear understanding can take critical systems offline instantly. These failures are avoidable, yet they remain common across mid-sized Australian businesses.
Change management exists to prevent these outages. It provides the structure needed to implement changes safely, predictably, and with accountability. When this structure is missing, IT environments become unstable, incident rates increase, and root-cause analysis often points back to uncontrolled changes.
A mature change control framework includes:
Documented change procedures, covering standard, normal, and emergency changes.
Formal change requests capturing intent, scope, and affected systems.
Risk and impact assessments to understand operational consequences before implementation.
Approval workflows, ensuring oversight from appropriate stakeholders.
Pre-change communication, especially when user impact is expected.
Rollback plans that allow changes to be reversed quickly if issues arise.
Post-implementation validation to confirm systems behave as expected.
These requirements are not bureaucracy; they are safeguards. Frameworks like the ACSC ISM and ITIL treat structured change management as essential for maintaining environmental stability and reducing security risk.
Inconsistent or undocumented change practices create configuration drift, break dependencies, and open vulnerabilities that attackers can exploit. More importantly, they reduce leadership’s ability to demonstrate due diligence in the event of an outage or regulatory review.
Tactical takeaway: Ask your IT manager to walk you through your current change management process. If there is no documented procedure with defined approval workflows and rollback steps, formalising this process should be an immediate priority.
Controlled change is one of the strongest indicators of a well-run IT operation.
How Beyond Technology Elevates Operational Resilience Through Evidence-Based Controls
Operational resilience is not determined by how well systems run on a good day — it’s determined by how predictably they behave when something goes wrong. Backup recoverability and change management discipline are two of the most critical controls influencing that predictability. Yet most organisations struggle to maintain them consistently because ownership is unclear, processes drift over time, and there is no structured model for ongoing validation.
Beyond Technology’s approach closes these gaps by replacing assumptions with evidence and turning informal practices into defensible, repeatable controls.
Our uplift program includes:
Backup & Recovery Maturity Assessment
Reviewing backup configurations, schedules, and retention policies
Reviewing recovery plans, and ensuring testing full restorations validate RTO/RPO alignment
Identifying gaps in evidence, procedures, tooling, and documentation
Creating a structured restoration test calendar and reporting model
Change Management Framework Development
Designing fit-for-purpose change procedures aligned to ISM and ITIL
Establishing approval workflows, communication steps, and rollback definitions
Embedding risk and impact assessment into every change type
Integrating change governance into IT operational rhythms
Governance & Assurance
Creating dashboards and evidence packs for audit and board reporting
Establishing clear control owners and review cycles
Conducting periodic assurance reviews to prevent drift
Our goal is simple: build operational controls that hold up under pressure — during incidents, during audits, and during executive scrutiny.
With Beyond Technology’s guidance, organisations gain the confidence that they can restore systems when it matters most and implement changes without destabilising the environment. This is the foundation of operational resilience.
Final Thoughts: Resilience Depends on Controls That Work When Tested
Backup and change controls are often treated as operational hygiene, but they are far more than that — they are the safeguards that determine whether an organisation can withstand disruption without prolonged impact. Backups and redundancy protect business continuity, but only if restoration can be proven. Change management protects system stability, but only when the process is structured, documented, and consistently applied.
Organisations that rely on informal processes or untested assumptions are exposed the moment something goes wrong. Regulators and insurers increasingly expect leaders to demonstrate not just intent, but evidence that these controls function in practice.
Beyond Technology helps organisations build this operational resilience by turning control frameworks into consistent, measurable disciplines. We replace undocumented processes with structured governance, uplift technical capability, and embed ongoing assurance so controls remain effective as environments evolve.
Resilience is not built reactively — it is built through deliberate governance and regular validation. Strengthening backup and change controls is one of the most impactful steps an organisation can take to reduce downtime, limit risk, and operate with confidence.
FAQs Answered
1. Why is regular backup recovery and redundancy testing essential for operational resilience?
Backup recovery testing confirms that data can actually be restored when it matters. Many organisations assume their backups will work but have never validated them. Regular restoration and redundancy testing ensures recovery times meet business expectations, identifies gaps before a crisis occurs, and provides evidence of due diligence. Without testing, backup success is based on hope, not certainty.
2. How often should organisations perform full backup restoration and redundancy tests?
Full restoration tests should occur at least every six months, with more frequent testing for business-critical systems. Testing verifies RTO and RPO targets, confirms data integrity, and ensures teams know the recovery process end to end. Regular validation reduces downtime risk and is a key expectation under frameworks such as the ACSC Essential Eight.
3. What should a formal change management process include?
A formal change process includes documented change requests, risk and impact assessments, approvals, communication plans, rollback procedures, and post-implementation validation. These steps ensure changes are introduced safely and predictably. A structured process reduces outages, prevents configuration drift, and provides the evidence regulators and auditors expect to see.
4. Why do poorly controlled IT changes cause so many outages?
Uncontrolled changes bypass essential safeguards. Without risk assessment, approvals, or rollback planning, even small changes can break dependencies, expose vulnerabilities, or take critical systems offline. Most self-inflicted outages stem from informal or undocumented changes. A disciplined change process greatly reduces operational disruption and strengthens governance.
5. What frameworks guide best practice for backup governance and change control in Australia?
The ACSC Essential Eight and industry standards defines expectations for backup frequency, testing, and secure restoration. The ACSC Information Security Manual (ISM) outlines detailed controls for change management, system updates, and configuration governance. Together, these frameworks provide a strong benchmark for operational resilience and audit readiness.
6. How does Beyond Technology help organisations strengthen their backup and change management controls?
Beyond Technology assesses the effectiveness of backup and change controls, identifies operational gaps, and designs uplift programs aligned to Essential Eight and ISM standards. We develop backup standards, implement recovery testing cycles, establish formal change processes, and embed governance structures that provide evidence of control effectiveness. Our approach improves stability, reduces outage risk, and strengthens organisational resilience.
A 30-minute conversation with a partner is the simplest way to see where your organisation stands. No pitch, no sales process – just a senior view of where you are and where the priorities should sit.